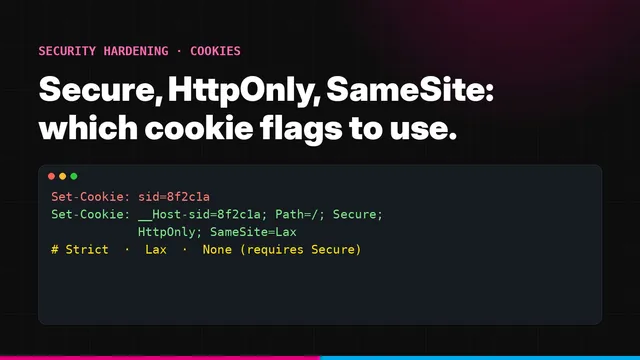
Secure, HttpOnly and SameSite cookies: which flags Sumrite sets and why.
Secure, HttpOnly, SameSite Strict, Lax or None: what each flag does, which one each cookie should use, and how to set them in your stack.
By Niyaz Khan9 min read
Field notes
Case studies, hardening guides and compliance explainers from Sumrite penetration testers. No scanner dumps.
Secure, HttpOnly, SameSite Strict, Lax or None: what each flag does, which one each cookie should use, and how to set them in your stack.
By Niyaz Khan9 min read
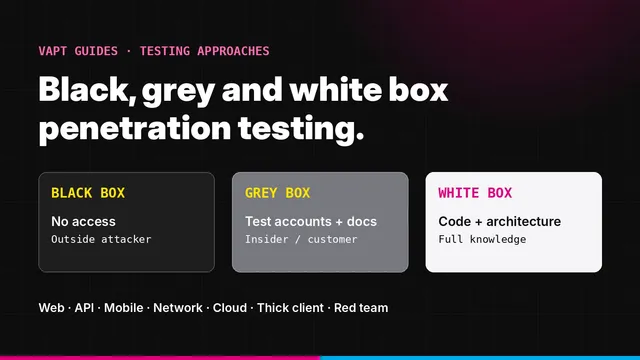
VAPT explained in plain language: the difference between VA and PT, the types of testing, how an assessment runs, what it costs and when you need one.
By Faisal Khan10 min read
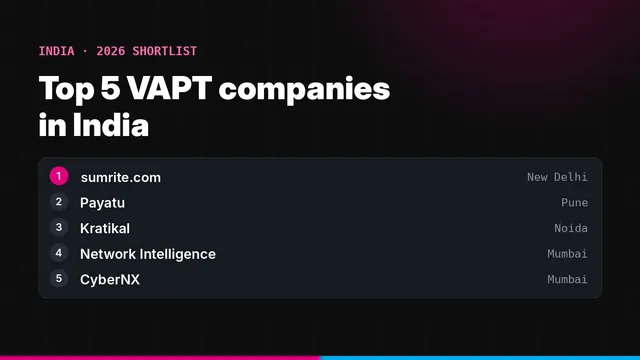
Ten VAPT service providers in India compared on services, credentials and best fit, with a buyer's checklist and the questions to ask before you sign.
By Faisal Khan11 min read
PTaaS delivers expert-led penetration testing continuously through a platform, with live findings, Jira and GitHub sync, on-demand retests and audit-ready reports.
By Faisal Khan2 min read
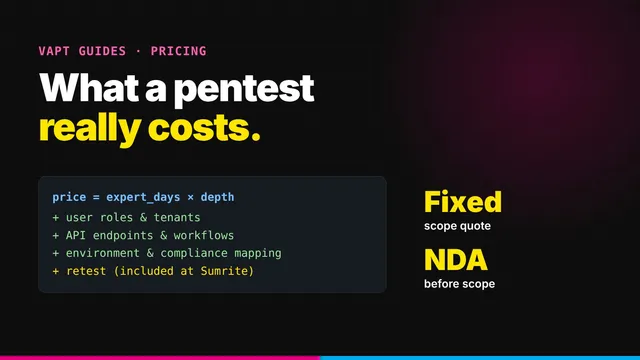
VAPT pricing follows effort, not tools. Learn what drives cost, how to compare quotes and why a cheap scan-only report costs more later.
By Faisal Khan2 min read
Who must comply with NCA's Critical Systems Cybersecurity Controls (CSCC-1:2019), how critical systems are identified, and the testing cadence and evidence CSCC expects.
By Nishant Sharma7 min read
The Saudi PDPL penalty ceiling, when fines double, the 72-hour breach notice, what SDAIA's 48 decisions penalised and a 90-day plan to be ready for a notice.
By Faisal Khan8 min read
What SAMA CSF 3.2.4 requires, how often banks and fintechs must test, what to scope, the evidence to keep, and the mistakes we see most in Saudi banks.
By Faisal Khan7 min read
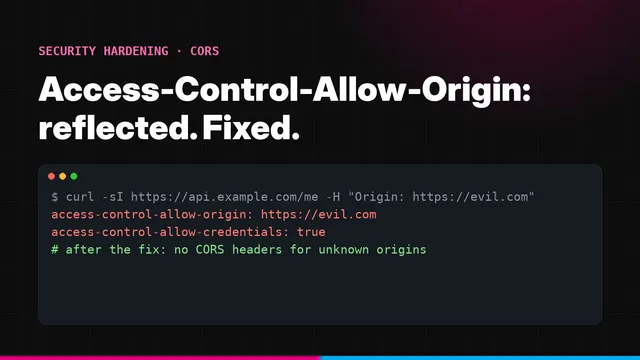
We sent Origin: evil.com and the API echoed it back with credentials allowed. Why that matters and how to fix it in every common stack.
By Niyaz Khan10 min read
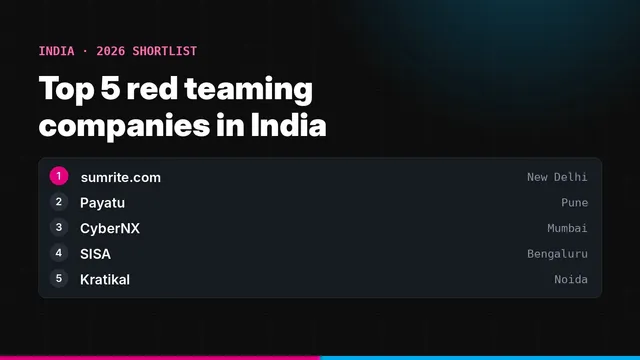
Five red teaming providers in India compared, how red teaming differs from VAPT, what an engagement looks like and the questions to ask before you hire.
By Faisal Khan7 min read
Testing days, reporting and retest: realistic penetration test timelines by scope, and how Sumrite delivers a scoped web or API report in 48 hours.
By Faisal Khan1 min read
Scope, methodology, findings, retest letter and criteria mapping: what goes into a SOC 2 penetration test report and what your auditor looks for.
By Nishant Sharma9 min read
Talk to a tester
Fixed-scope quote. Expert-led testing, verified findings, a fix-and-retest cycle and a report your auditors can use as evidence.