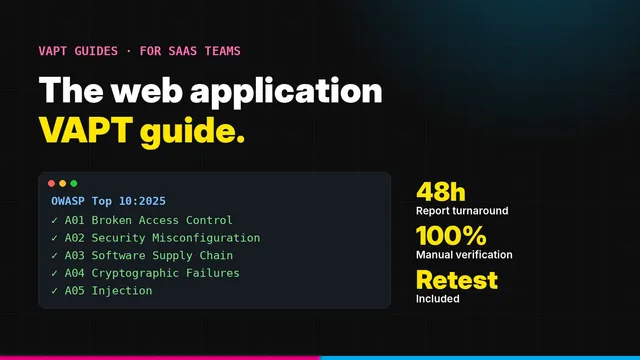
48-Hour Report Delivery

Prove your product is secure.
VAPT report in 48 hours.

Expert-led penetration testing that goes beyond the scanner: broken access control, business logic and chained attacks. Every finding verified by a security expert, every fix retested, and a report your auditors and enterprise buyers can use as evidence.

  • Expert-led testing, no scanner dumps
  • Retest included
  • NDA before scope
  • Mapped to 23 frameworks
48h
Report turnaround
250+
Clients cleared through audits
23
Compliance frameworks mapped
$0
Your first scan, at scan.sumrite.com
It happens more than you think

Need a VAPT report before your next audit?

Three situations we solve every week, each with a tight deadline and a lot at stake. Hover a card for a glimpse of how it plays out.

01

Client onboarding

Your enterprise client won't sign until you hand over a VAPT report. Their security team needs it before procurement can proceed.

How startups clear buyer security reviews →
02

Security questionnaires

You're filling out a 40-question vendor security form and one section asks for proof of penetration testing. You need a credible report to attach.

See a sample report →
03

Compliance requirements

SOC 2 Type 2, ISO 27001, PCI DSS, HIPAA, GDPR, NCA and PDPL, DIFC and ADGM, DORA, APRA CPS 234, ST4S or a government tender: 23 frameworks across five regions, and each one wants documented evidence of security testing by a credible third party.

Browse all 23 framework guides →
Free scan · Expert testing

The scanner part is free. The part that protects you is ours.

Many firms sell scanner output as a penetration test. We give that layer away at scan.sumrite.com, and you pay Summit for what only an expert finds.

Free · scan.sumrite.com

Scanner-level issues, in minutes

Point our autonomous scanner at your site. No sales call, no card. You get the class of report other firms charge for.

  • Missing Content-Security-PolicyNo CSP header to limit what scripts can run
  • HSTS not enforcedBrowsers are not forced onto HTTPS
  • Server header disclosedYour web server and version on show
  • Clickjacking protection missingNo X-Frame-Options or frame-ancestors rule
  • Cookie and header misconfigurationsWeak flags and other header-level gaps
Run a free scan →
Expert-led · Summit

What only an expert finds

These are the flaws that leak customer data and sink audits. They take someone who understands how your product is meant to work, and then breaks it.

  • Broken access controlOne user reading another account's records
  • Business logic abuseSkipping a payment step or replaying a voucher
  • API authorisation flawsChanging an ID to reach another tenant's data
  • Chained attacksSmall issues combined into account takeover
  • Verified, real-world impactEvery finding proven, rated and explained
Get a Quote in 15 mins →

Free scan for scanner-level issues. Expert-led testing for everything a scanner can't see.

Why many VAPT reports are just scanner output

What we test

Every attack surface, one accountable team.

Nine services, one methodology. The testers who find the issues are the people who explain them to your engineers and your auditors.

01 / 09

Web Application VAPT

Authenticated, multi-role testing of your web app against the OWASP Top 10 and the business logic scanners never reach.

Explore Web Application VAPT →
02 / 09

API Security Testing

REST and GraphQL APIs tested for broken object-level authorisation, auth flaws and data exposure.

Explore API Security Testing →
03 / 09

Mobile App VAPT

iOS and Android apps and their back ends, tested against OWASP MASVS.

Explore Mobile App VAPT →
04 / 09

Network VAPT

External and internal infrastructure, Active Directory and exposed services, tested the way an attacker would.

Explore Network VAPT →
05 / 09

Cloud Security Assessment

AWS, Azure and GCP configuration, identity and exposure reviewed against CIS Benchmarks.

Explore Cloud Security Assessment →
06 / 09

Source Code Review

Expert review of the code paths that matter: authentication, access control, input handling and secrets.

Explore Source Code Review →
07 / 09

Thick Client VAPT

Desktop applications, their local storage and the servers they talk to.

Explore Thick Client VAPT →
08 / 09

Phishing Simulations

Realistic campaigns that measure how your people respond, with training that follows.

Explore Phishing Simulations →
09 / 09

Red Team Operations

Objective-based attack simulation that tests whether your team detects and stops a real adversary.

Explore Red Team Operations →
Compare all services →
Simple process

Your Security Testing Journey

Choose what you want tested to see every step, from scope and NDA to a retested, final report. No jargon, no surprises.

Web Application VAPTService details →
Step 1 of 6

Request your web app test

Submit your scope so our team can plan the engagement and get started, often the same day.

  • Share application URLs, environments and user roles
  • Test accounts for each role: standard user, admin, a second tenant
  • Tell us the goal: SOC 2, ISO 27001, PCI DSS, a buyer review or a launch
  • NDA and testing authorisation signed before any technical detail
Step 2 of 6

Expert assessment: Web Application VAPT

Every phase is run by a security expert, with tools used only to speed up the routine parts. Findings are reproduced and confirmed before they reach your report.

Recon and mapping

  • Application and attack-surface mapping
  • Framework and technology fingerprinting
  • Role and permission matrix built from your accounts

Authentication and sessions

  • Login, MFA and password-reset abuse
  • Token handling, session fixation, logout and expiry
  • SSO and OAuth flow tampering

Access control

  • Horizontal and vertical privilege escalation
  • IDOR: swapping identifiers across accounts and tenants
  • Forced browsing to admin and hidden functions

Input handling

  • SQL, NoSQL and command injection
  • Stored, reflected and DOM XSS, plus CSRF
  • SSRF, XXE, file upload and deserialisation

Business logic

  • Payment, coupon and workflow bypass
  • Race conditions and request replay
  • Skipping steps in multi-step flows
Expert-only work: beyond scanners and AI
  • Learning what your app is supposed to do, then breaking it
  • Chaining low-severity issues into a real breach
  • Judging business impact, not just a CVSS number
  • Bypassing custom controls and WAF rules by hand
Step 3 of 6

Draft report in 48 hours

Findings are written for two readers at once: developers who need the exact fix and auditors or buyers who need confidence.

  • Executive summary for leadership and auditors
  • CVSS-rated findings with proof of exploitation
  • Step-by-step reproduction for your engineers
  • Mapped to the framework you named in scope
Step 4 of 6

Fix the vulnerabilities

Your team fixes the issues with guidance written for your stack, and the tester who found each issue answers questions directly.

  • Fix guidance per finding, in plain language
  • Prioritised order so critical issues go first
  • Direct line to the tester, no account-manager relay
Step 5 of 6

Re-validation, included

Every fix is tested again. Nothing is marked closed on trust.

  • Each fix re-tested, with before and after evidence
  • Regression checks on related functionality
  • Status per finding: fixed, partly fixed or open
  • Retest included at no extra cost
Step 6 of 6

Final report issued

You receive a verified report in your company name, ready for clients, auditors and procurement.

  • Issued in your company name
  • Updated with retest results
  • Dated and scoped to the assets tested
  • Re-issued after major product changes
API Security TestingService details →
Step 1 of 6

Request your api test

Submit your scope so our team can plan the engagement and get started, often the same day.

  • Share the OpenAPI or Swagger file, Postman collection or GraphQL schema
  • Tokens or keys for each role and tenant
  • List who consumes the API: web, mobile, partners
  • NDA and testing authorisation signed first
Step 2 of 6

Expert assessment: API Security Testing

Every phase is run by a security expert, with tools used only to speed up the routine parts. Findings are reproduced and confirmed before they reach your report.

Discovery

  • Endpoint and parameter enumeration, including legacy versions
  • Schema introspection and shadow-API discovery

Authorisation

  • Object-level checks on every identifier (BOLA)
  • Function-level: calling admin endpoints as a normal user
  • Property-level exposure and mass assignment

Authentication and tokens

  • JWT and OAuth weaknesses: weak secrets, scope abuse
  • API key handling and rotation
  • Rate-limit and brute-force controls

Data exposure and injection

  • Excessive data returned in responses
  • Injection in JSON and GraphQL, including batching and depth abuse
  • SSRF through URL parameters and webhooks

Business-flow abuse

  • Abusing sign-up, checkout and voucher flows at scale
  • Replay and race conditions
Expert-only work: beyond scanners and AI
  • Working out which objects belong to which tenant, then crossing the line
  • Chaining a small data leak into account takeover
  • Reasoning about authorisation field by field in GraphQL
  • Abusing intended features in ways the spec never imagined
Step 3 of 6

Draft report in 48 hours

Findings are written for two readers at once: developers who need the exact fix and auditors or buyers who need confidence.

  • Executive summary for leadership and auditors
  • CVSS-rated findings with proof of exploitation
  • Step-by-step reproduction for your engineers
  • Mapped to the framework you named in scope
Step 4 of 6

Fix the vulnerabilities

Your team fixes the issues with guidance written for your stack, and the tester who found each issue answers questions directly.

  • Fix guidance per finding, in plain language
  • Prioritised order so critical issues go first
  • Direct line to the tester, no account-manager relay
Step 5 of 6

Re-validation, included

Every fix is tested again. Nothing is marked closed on trust.

  • Each fix re-tested, with before and after evidence
  • Regression checks on related functionality
  • Status per finding: fixed, partly fixed or open
  • Retest included at no extra cost
Step 6 of 6

Final report issued

You receive a verified report in your company name, ready for clients, auditors and procurement.

  • Issued in your company name
  • Updated with retest results
  • Dated and scoped to the assets tested
  • Re-issued after major product changes
Mobile App VAPTService details →
Step 1 of 6

Request your mobile test

Submit your scope so our team can plan the engagement and get started, often the same day.

  • Share iOS and Android builds (IPA, APK) or store links
  • Backend and API scope, with test accounts
  • Confirm platforms and minimum OS versions
  • NDA and testing authorisation signed first
Step 2 of 6

Expert assessment: Mobile App VAPT

Every phase is run by a security expert, with tools used only to speed up the routine parts. Findings are reproduced and confirmed before they reach your report.

Static analysis

  • Decompile and review the binary, manifest and entitlements
  • Hard-coded secrets, keys and endpoints
  • Insecure storage design and third-party SDK risk
  • Obfuscation and tamper-protection review

Dynamic analysis

  • Runtime instrumentation and hooking on rooted and jailbroken devices
  • Local storage, keychain, keystore, logs and clipboard
  • Certificate pinning and root or jailbreak detection bypass
  • Deep links, intents and inter-app communication abuse

Network and backend

  • Traffic interception and TLS validation
  • API authorisation behind the app: token reuse, BOLA
  • Server-side checks the client wrongly enforces

OWASP MASVS coverage

  • Storage, crypto, authentication, network, platform, code and resilience requirements
Expert-only work: beyond scanners and AI
  • Reverse-engineering custom protections and bypassing them live
  • Tracing a client-side control to the server check that should exist
  • Judging real exploitability on a lost or stolen device
  • Chaining an app weakness with an API flaw
Step 3 of 6

Draft report in 48 hours

Findings are written for two readers at once: developers who need the exact fix and auditors or buyers who need confidence.

  • Executive summary for leadership and auditors
  • CVSS-rated findings with proof of exploitation
  • Step-by-step reproduction for your engineers
  • Mapped to the framework you named in scope
Step 4 of 6

Fix the vulnerabilities

Your team fixes the issues with guidance written for your stack, and the tester who found each issue answers questions directly.

  • Fix guidance per finding, in plain language
  • Prioritised order so critical issues go first
  • Direct line to the tester, no account-manager relay
Step 5 of 6

Re-validation, included

Every fix is tested again. Nothing is marked closed on trust.

  • Each fix re-tested, with before and after evidence
  • Regression checks on related functionality
  • Status per finding: fixed, partly fixed or open
  • Retest included at no extra cost
Step 6 of 6

Final report issued

You receive a verified report in your company name, ready for clients, auditors and procurement.

  • Issued in your company name
  • Updated with retest results
  • Dated and scoped to the assets tested
  • Re-issued after major product changes
Step 1 of 6

Request your network test

Submit your scope so our team can plan the engagement and get started, often the same day.

  • External IP ranges and domains, plus internal segments
  • Agree test windows and safe-mode rules
  • VPN, jump host or on-site access for internal testing
  • Decide whether Active Directory is in scope; NDA signed first
Step 2 of 6

Expert assessment: Network VAPT

Every phase is run by a security expert, with tools used only to speed up the routine parts. Findings are reproduced and confirmed before they reach your report.

External exposure

  • Host and service discovery
  • Version and exposure analysis
  • Default credentials, exposed admin panels and management ports
  • VPN, mail and remote-access appliance review

Internal and Active Directory

  • Segmentation and lateral-movement paths
  • Kerberoasting, delegation and ACL abuse
  • Credential exposure and agreed-limit password spraying

Controlled exploitation

  • Proof of exploit on confirmed vulnerabilities
  • Privilege escalation, up to domain level where in scope

Hardening review

  • Firewall, protocol and encryption weaknesses against CIS Benchmarks
Expert-only work: beyond scanners and AI
  • Choosing the attack path a real intruder would take
  • Chaining a misconfiguration into domain compromise
  • Deciding what is safe to exploit in production
  • Reading what a scanner calls "informational" and seeing the risk
Step 3 of 6

Draft report in 48 hours

Findings are written for two readers at once: developers who need the exact fix and auditors or buyers who need confidence.

  • Executive summary for leadership and auditors
  • CVSS-rated findings with proof of exploitation
  • Step-by-step reproduction for your engineers
  • Mapped to the framework you named in scope
Step 4 of 6

Fix the vulnerabilities

Your team fixes the issues with guidance written for your stack, and the tester who found each issue answers questions directly.

  • Fix guidance per finding, in plain language
  • Prioritised order so critical issues go first
  • Direct line to the tester, no account-manager relay
Step 5 of 6

Re-validation, included

Every fix is tested again. Nothing is marked closed on trust.

  • Each fix re-tested, with before and after evidence
  • Regression checks on related functionality
  • Status per finding: fixed, partly fixed or open
  • Retest included at no extra cost
Step 6 of 6

Final report issued

You receive a verified report in your company name, ready for clients, auditors and procurement.

  • Issued in your company name
  • Updated with retest results
  • Dated and scoped to the assets tested
  • Re-issued after major product changes
Cloud Security AssessmentService details →
Step 1 of 6

Request your cloud test

Submit your scope so our team can plan the engagement and get started, often the same day.

  • AWS accounts, Azure subscriptions or GCP projects in scope
  • A read-only audit role, plus any test roles
  • Architecture overview and the workloads that matter most
  • NDA and testing authorisation signed first
Step 2 of 6

Expert assessment: Cloud Security Assessment

Every phase is run by a security expert, with tools used only to speed up the routine parts. Findings are reproduced and confirmed before they reach your report.

Identity and access

  • IAM policies, privilege-escalation paths and unused access
  • Role trust, federation and key hygiene
  • MFA and root or owner account protection

Exposure and data

  • Public storage, snapshots and databases
  • Security groups, public endpoints and load balancer headers
  • Encryption at rest and in transit, key management

Benchmarks

  • CIS Benchmarks for your provider
  • Logging, monitoring and alerting coverage

Workloads

  • Container, serverless and infrastructure-as-code misconfigurations
  • Secrets in environment variables and repositories
Expert-only work: beyond scanners and AI
  • Finding privilege-escalation chains across roles and services
  • Separating exploitable exposure from theoretical findings
  • Judging blast radius for your architecture
  • Reading design intent, not just resource flags
Step 3 of 6

Draft report in 48 hours

Findings are written for two readers at once: developers who need the exact fix and auditors or buyers who need confidence.

  • Executive summary for leadership and auditors
  • CVSS-rated findings with proof of exploitation
  • Step-by-step reproduction for your engineers
  • Mapped to the framework you named in scope
Step 4 of 6

Fix the vulnerabilities

Your team fixes the issues with guidance written for your stack, and the tester who found each issue answers questions directly.

  • Fix guidance per finding, in plain language
  • Prioritised order so critical issues go first
  • Direct line to the tester, no account-manager relay
Step 5 of 6

Re-validation, included

Every fix is tested again. Nothing is marked closed on trust.

  • Each fix re-tested, with before and after evidence
  • Regression checks on related functionality
  • Status per finding: fixed, partly fixed or open
  • Retest included at no extra cost
Step 6 of 6

Final report issued

You receive a verified report in your company name, ready for clients, auditors and procurement.

  • Issued in your company name
  • Updated with retest results
  • Dated and scoped to the assets tested
  • Re-issued after major product changes
Source Code ReviewService details →
Step 1 of 6

Request your source code test

Submit your scope so our team can plan the engagement and get started, often the same day.

  • Read-only repository access and the language and framework list
  • A walkthrough of architecture and trust boundaries
  • Priority areas: authentication, payments, personal data
  • NDA signed before any code is shared
Step 2 of 6

Expert assessment: Source Code Review

Every phase is run by a security expert, with tools used only to speed up the routine parts. Findings are reproduced and confirmed before they reach your report.

Threat-led mapping

  • Entry points, trust boundaries and sensitive data flows

Security-critical paths

  • Authentication, session and access-control logic
  • Input handling, injection sinks and deserialisation
  • Cryptography and secrets management

Dependencies and build

  • Vulnerable and abandoned dependencies
  • CI/CD pipelines, build scripts and leaked secrets

Validation

  • Confirming exploitable findings against a running build where possible
Expert-only work: beyond scanners and AI
  • Understanding what the developer intended and where it breaks
  • Spotting logic flaws that no pattern-matcher flags
  • Separating reachable vulnerabilities from dead code
  • Reviewing custom crypto and authorisation frameworks
Step 3 of 6

Draft report in 48 hours

Findings are written for two readers at once: developers who need the exact fix and auditors or buyers who need confidence.

  • Executive summary for leadership and auditors
  • CVSS-rated findings with proof of exploitation
  • Step-by-step reproduction for your engineers
  • Mapped to the framework you named in scope
Step 4 of 6

Fix the vulnerabilities

Your team fixes the issues with guidance written for your stack, and the tester who found each issue answers questions directly.

  • Fix guidance per finding, in plain language
  • Prioritised order so critical issues go first
  • Direct line to the tester, no account-manager relay
Step 5 of 6

Re-validation, included

Every fix is tested again. Nothing is marked closed on trust.

  • Each fix re-tested, with before and after evidence
  • Regression checks on related functionality
  • Status per finding: fixed, partly fixed or open
  • Retest included at no extra cost
Step 6 of 6

Final report issued

You receive a verified report in your company name, ready for clients, auditors and procurement.

  • Issued in your company name
  • Updated with retest results
  • Dated and scoped to the assets tested
  • Re-issued after major product changes
Thick Client VAPTService details →
Step 1 of 6

Request your thick client test

Submit your scope so our team can plan the engagement and get started, often the same day.

  • Installer or build and the supported operating systems
  • The servers and APIs the client talks to
  • Test accounts and licence keys
  • NDA and testing authorisation signed first
Step 2 of 6

Expert assessment: Thick Client VAPT

Every phase is run by a security expert, with tools used only to speed up the routine parts. Findings are reproduced and confirmed before they reach your report.

Static and binary

  • Decompile .NET, Java and native binaries
  • Hard-coded credentials, keys and connection strings
  • DLL hijacking, side-loading and installer permissions

Local and runtime

  • Local storage, registry, configuration files and memory
  • Process hooking and tampering
  • Licence and client-side control bypass

Network and server

  • Interception of proxy-unaware and non-HTTP traffic
  • Server-side authorisation the client simply assumes
Expert-only work: beyond scanners and AI
  • Reverse-engineering custom protocols
  • Hooking the client to test how far the server trusts it
  • Recovering credentials from memory
  • Chaining a local weakness into server compromise
Step 3 of 6

Draft report in 48 hours

Findings are written for two readers at once: developers who need the exact fix and auditors or buyers who need confidence.

  • Executive summary for leadership and auditors
  • CVSS-rated findings with proof of exploitation
  • Step-by-step reproduction for your engineers
  • Mapped to the framework you named in scope
Step 4 of 6

Fix the vulnerabilities

Your team fixes the issues with guidance written for your stack, and the tester who found each issue answers questions directly.

  • Fix guidance per finding, in plain language
  • Prioritised order so critical issues go first
  • Direct line to the tester, no account-manager relay
Step 5 of 6

Re-validation, included

Every fix is tested again. Nothing is marked closed on trust.

  • Each fix re-tested, with before and after evidence
  • Regression checks on related functionality
  • Status per finding: fixed, partly fixed or open
  • Retest included at no extra cost
Step 6 of 6

Final report issued

You receive a verified report in your company name, ready for clients, auditors and procurement.

  • Issued in your company name
  • Updated with retest results
  • Dated and scoped to the assets tested
  • Re-issued after major product changes
Phishing SimulationsService details →
Step 1 of 6

Request your phishing test

Submit your scope so our team can plan the engagement and get started, often the same day.

  • Agree objectives, target groups and exclusions
  • HR and legal sign-off, plus emergency contacts
  • Approve the pretexts and look-alike brands
  • NDA signed before any employee data is shared
Step 2 of 6

Expert assessment: Phishing Simulations

Every phase is run by a security expert, with tools used only to speed up the routine parts. Findings are reproduced and confirmed before they reach your report.

Campaign design

  • Pretexts tuned to your industry and roles
  • Domain, mail-authentication and landing-page setup

Delivery and measurement

  • Staged sends with click, credential-submit and report-rate tracking
  • MFA-prompt and attachment scenarios where agreed

Training that follows

  • Just-in-time guidance for people who engage
  • Plain-language awareness material for the wider team
Expert-only work: beyond scanners and AI
  • Writing believable pretexts around your real business
  • Judging what a motivated attacker would try next
  • Getting past mail filters with careful tradecraft
  • Handling the people involved with care
Step 3 of 6

Draft report in 48 hours

Findings are written for two readers at once: developers who need the exact fix and auditors or buyers who need confidence.

  • Executive summary for leadership and auditors
  • CVSS-rated findings with proof of exploitation
  • Step-by-step reproduction for your engineers
  • Mapped to the framework you named in scope
Step 4 of 6

Fix the vulnerabilities

Your team fixes the issues with guidance written for your stack, and the tester who found each issue answers questions directly.

  • Fix guidance per finding, in plain language
  • Prioritised order so critical issues go first
  • Direct line to the tester, no account-manager relay
Step 5 of 6

Re-validation, included

Every fix is tested again. Nothing is marked closed on trust.

  • Each fix re-tested, with before and after evidence
  • Regression checks on related functionality
  • Status per finding: fixed, partly fixed or open
  • Retest included at no extra cost
Step 6 of 6

Final report issued

You receive a verified report in your company name, ready for clients, auditors and procurement.

  • Issued in your company name
  • Updated with retest results
  • Dated and scoped to the assets tested
  • Re-issued after major product changes
Red Team OperationsService details →
Step 1 of 6

Request your red team test

Submit your scope so our team can plan the engagement and get started, often the same day.

  • Agree the objective: the crown jewels an attacker would go for
  • Rules of engagement and escalation paths
  • Deconfliction contacts and anything off-limits
  • NDA and written authorisation signed first
Step 2 of 6

Expert assessment: Red Team Operations

Every phase is run by a security expert, with tools used only to speed up the routine parts. Findings are reproduced and confirmed before they reach your report.

Recon and initial access

  • Open-source intelligence and attack-surface discovery
  • Phishing, credential and external-compromise paths

Post-compromise

  • Privilege escalation and lateral movement
  • Identity and cloud attack paths
  • Persistence and evasion, mapped to MITRE ATT&CK

Objective and detection

  • Reaching the agreed objective
  • Recording what your team saw, missed and stopped
Expert-only work: beyond scanners and AI
  • Adapting live to your defenders
  • Operating quietly enough to test detection
  • Combining social and technical paths where agreed
  • Turning a campaign into a defence roadmap
Step 3 of 6

Draft report in 48 hours

Findings are written for two readers at once: developers who need the exact fix and auditors or buyers who need confidence.

  • Executive summary for leadership and auditors
  • CVSS-rated findings with proof of exploitation
  • Step-by-step reproduction for your engineers
  • Mapped to the framework you named in scope
Step 4 of 6

Fix the vulnerabilities

Your team fixes the issues with guidance written for your stack, and the tester who found each issue answers questions directly.

  • Fix guidance per finding, in plain language
  • Prioritised order so critical issues go first
  • Direct line to the tester, no account-manager relay
Step 5 of 6

Re-validation, included

Every fix is tested again. Nothing is marked closed on trust.

  • Each fix re-tested, with before and after evidence
  • Regression checks on related functionality
  • Status per finding: fixed, partly fixed or open
  • Retest included at no extra cost
Step 6 of 6

Final report issued

You receive a verified report in your company name, ready for clients, auditors and procurement.

  • Issued in your company name
  • Updated with retest results
  • Dated and scoped to the assets tested
  • Re-issued after major product changes
Real scenarios

The breach you haven't had yet costs far less to prevent.

Real scenario · Client data leaked

"We built fast and shipped. We never thought to check if one user could access another user's data. They could. All of it."

SaaS founder · Came to us after a client noticed seeing another company's invoices

A single access control vulnerability let any logged-in user change an ID in the URL and view any other account's data. No hacking skills required. Just curiosity. One of the most common and damaging flaws in web apps today.

How Summit Would Have Helped
Caught before launchExpert testing checks every data access path, not just the obvious ones.
Clear fix, same dayExact location, exact fix. No confusion, no upselling.
Report to show clientsProof that you take their data seriously — before they have to ask.
02
Enterprise deal at risk

Your biggest client just asked for a security report.

You're in UAT. Deal almost closed. Their security team asks for a VAPT report. You have 48 hours. This is the #1 reason startups come to us.

Get Report in 48h →
03

Launching in 2 weeks? Ship with confidence.

Pre-launch testing means your first impression is a secure one. Find issues before your users — or attackers — do. One engagement, full coverage, report on delivery.

Book Pre-launch Test →
Industry Standard Methodology
OWASP Top 10 Web
OWASP Testing Guide v4.2
OWASP API Security Top 10
OWASP MASVS iOS & Android
NIST SP 800-115
P
PTES Standard
CIS Benchmarks
Why clients choose us

What makes a VAPT report actually worth paying for

Not all reports are equal. Here is the difference between a report that sits in a drawer and one that protects your business and closes your deals.

01 / 06

Expert-led testing, not scanner output

Scanners catch missing headers. They miss broken access control, business logic flaws and chained attacks. Every finding in a Summit report is verified by a security expert.

02 / 06

Report in 48 hours, not 3 weeks

Most firms take 2 to 4 weeks. We deliver your full report within 48 hours — without cutting corners. Built for startup timelines.

03 / 06

Reports clients and auditors trust

Written for two audiences: developers who need exact fixes, and clients or auditors who need confidence. One report, two purposes, no jargon.

04 / 06

Re-testing included, always

Fixed the issues? We re-test at no extra charge and update your report. Your clients get assurance that vulnerabilities were properly resolved.

05 / 06

Plain language, always

Every finding explained in plain language — what it means for your business and users. Developers love the fix guides. No unexplained acronyms.

06 / 06

Report you can actually use

Built to support compliance audits, enterprise onboarding and vendor questionnaires. Issued in your company name.

Read: what makes a VAPT report worth paying for →
Research & Findings

Real vulnerabilities. Real write-ups.

Case studies and field guides from our testing team. No theory, just what we found and how to fix it.
Expert-Verified Findings

Your report.
48 hours.

Get the security report your clients are asking for, backed by testing from security experts who know exactly what they are doing.

No commitment · Response within 15 minutes · NDA signed before scoping
Summit at a glance

A penetration testing company built for deadlines.

Summit is an expert-led security testing and compliance firm serving SaaS, fintech and enterprise teams worldwide. We test the way attackers think, verify every finding, and write reports that leadership, engineers and auditors can each act on.

About Summit →Read our research →
What we do
Expert-led VAPT in 48 hours for web apps, APIs, mobile, networks and cloud, plus source code review, phishing simulations and red team operations, with every report mapped to the compliance framework you need evidence for.
Turnaround
Quote within 15 minutes; a standard web app or API report in 48 hours. Retest of fixed findings included.
Standards
OWASP Testing Guide, OWASP API and Mobile (MASVS), NIST SP 800-115, PTES and CIS Benchmarks.
Compliance
23 frameworks across five regions: SOC 1 and SOC 2, ISO 27001, PCI DSS, HIPAA, NIST CSF, GDPR, DORA and NIS2, NCA ECC, CCC and DCC, SAMA, the Saudi, UAE, Omani, Qatari, Bahraini and Egyptian data protection laws, DIFC and ADGM, India’s DPDP Act, SEBI and RBI, APRA CPS 230 and 234, the Australian Privacy Act and ST4S. See all frameworks →
Free tool
Scanner-level checks at no cost: scan.sumrite.com
Leadership
Faisal Khan, Director · faisal@sumrite.com
Address
E-211 FFC, III, Okhla Industrial Estate, New Delhi, Delhi 110020, India
Contact
sales@sumrite.com · +91 98113 63400 · WhatsApp
FAQ

VAPT and penetration testing: common questions

Straight answers about scope, timing, cost and what the report covers, each linked to a deeper guide.

14 questions

What is a VAPT report?

A VAPT report is a formal document issued after a completed vulnerability assessment and penetration test. It confirms that your application has been tested by a qualified security expert following recognised standards. It is commonly used as evidence for SOC 2 Type 2 audits, ISO 27001 vendor assessments, PCI DSS requirements, enterprise client onboarding questionnaires, and regulatory reviews such as DIFC and ADGM.

How long does a penetration test take?

Summit delivers a complete VAPT report within 48 hours of engagement start for standard web application and API tests. Complex applications, cloud infrastructure reviews, or red team operations may take 3 to 5 days. The industry average is 2 to 4 weeks. We are significantly faster without cutting corners because there is no sales or project management layer between the expert and the report.

Which compliance frameworks does a Summit VAPT report satisfy?

Summit reports are mapped to 23 frameworks across five regions: SOC 2, SOC 1, ISO 27001, PCI DSS, HIPAA and NIST CSF worldwide; GDPR, DORA, NIS2 and the Cyber Resilience Act in Europe; NCA ECC, CCC and DCC, SAMA, the Saudi, UAE, Omani, Qatari, Bahraini and Egyptian data protection laws, and DIFC and ADGM in the Middle East; the DPDP Act, SEBI CSCRF and RBI in India; and APRA CPS 230 and 234, the Australian Privacy Act and ST4S in Asia-Pacific. Enterprise onboarding questionnaires and government tender requirements are covered too.

Do you use automated scanners?

We use automation for what it does well: routine checks such as missing security headers, exposed server details and known-vulnerable components. That layer is free at scan.sumrite.com. Everything in a Summit report beyond it is found and verified by a security expert following OWASP Testing Guide v4.2, NIST SP 800-115 and PTES. We never hand over raw scanner output as a penetration test, because scanners miss business logic flaws, access control issues and chained vulnerabilities.

Is the scan at scan.sumrite.com really free?

Yes. Run it with no card and no sales call. It checks for scanner-level issues such as a missing Content-Security-Policy, HSTS not enforced, a disclosed Server header and missing clickjacking protection, so you can see where you stand before you talk to us. For the flaws a scanner cannot see, our experts take over.

How much does a VAPT cost?

Summit provides fixed-price quotes scoped to your application. Contact us at sumrite.com/contact and receive a quote within 15 minutes. There is no commitment required to receive a quote and we sign an NDA before any technical discussion.

What is the difference between VAPT and a vulnerability scan?

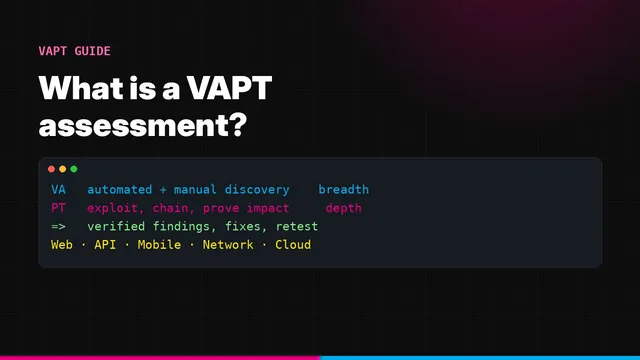
A vulnerability scan uses automated tools to identify known issues by pattern matching. A VAPT adds expert testing: chaining vulnerabilities, abusing business logic and verifying every finding by hand. The scan finds the checklist items; the expert finds the flaws that actually matter to your business and your clients.

Can you provide a VAPT report for UAE or Dubai compliance?

Yes. Summit provides VAPT reports that UAE teams use as technical evidence in DIFC, ADGM and CBUAE reviews. We serve clients across the Gulf region including UAE, Saudi Arabia, Qatar, Bahrain, and Kuwait. Reports are delivered remotely within 48 hours.

What is included in a Summit VAPT report?

A Summit VAPT report includes an executive summary for non-technical stakeholders, a detailed technical section with every finding, CVSS severity scores, step-by-step proof of concept for each vulnerability, developer-ready fix guidance in plain language, a remediation timeline, and a signed security report. Re-testing after fixes is included at no extra cost.

What types of applications does Summit test?

Summit tests web applications, REST and GraphQL APIs, iOS and Android mobile apps, cloud infrastructure on AWS, GCP, and Azure, internal networks, source code, thick client applications, phishing simulations, and performs red team operations simulating real attackers.

Do you work with startups?

Yes. Most of our clients are SaaS companies, fintech startups, and B2B software teams between seed and Series B. Security testing is often triggered by an enterprise client requiring a VAPT report before onboarding, a compliance audit, or a product launch. We are faster and more pragmatic than traditional security firms.

Where is Summit based?

Summit is based at E-211 FFC, III, Okhla Industrial Estate, New Delhi, Delhi 110020, India. Testing is delivered remotely, so we work with clients across India, the Gulf, Europe, Australia and North America.

Does Summit offer red team assessments?

Yes. Summit runs objective-based red team operations that combine phishing, external compromise, identity and cloud attack paths and lateral movement, mapped to MITRE ATT&CK, to test whether your team detects and stops a real attacker. Most organisations start with regular VAPT and add red teaming once that is in place.

Does SOC 2 or ISO 27001 require a VAPT?

Neither standard uses the words penetration test, but auditors routinely expect one. SOC 2 lists penetration testing as a point of focus under CC4.1, and ISO 27001 Annex A 8.8 requires technical vulnerabilities to be found and treated. An annual independent VAPT with a retest is the usual evidence.

See all FAQs →