Indian SaaS and consumer apps
Any digital product collecting users’ personal data needs notice, consent and safeguards.
Penalties under the DPDP Act reach ₹250 crore for failing to protect personal data. You can’t protect what you haven’t found, so start with Sumrite’s free PII discovery tool, then let our team test and evidence the safeguards the Act requires.
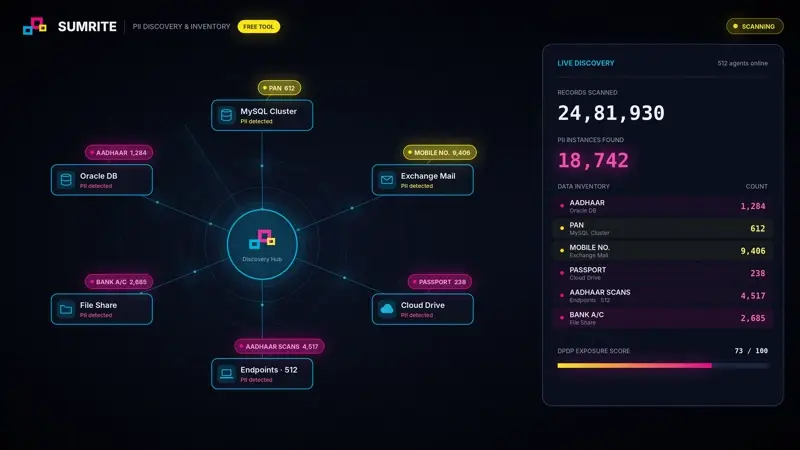
Every DPDP programme starts with one question: where is our personal data? Sumrite’s PII discovery and inventory tool answers it before you spend a rupee. An admin portal runs inside your network and agents scan databases, email, cloud drives, file shares and endpoints.
 100% free
The Schedule to the DPDP Act sets seven penalty lines. They are maximums, decided by the Data Protection Board case by case on the nature, gravity and duration of the breach, and they can apply together.
Source: Schedule to the Digital Personal Data Protection Act, 2023 (section 33). Breaching a Data Principal’s own duties carries up to ₹10,000; breaching a voluntary undertaking carries the penalty for the original breach.
₹250 cr vs ₹0Every line above starts with personal data you didn’t know you had. Finding it is free.
The Digital Personal Data Protection Act, 2023 sets rules for processing digital personal data in India, and outside India when goods or services are offered to people in India. It calls the organisation that decides the purpose and means of processing a Data Fiduciary, and the person the data is about a Data Principal.
The core model is notice and consent. Fiduciaries must tell people what data they collect and why, obtain clear consent for that purpose, and collect no more than necessary. There are limited “legitimate uses” in which consent is not needed, and verifiable parental consent is required for children’s data.
Section 8(5) requires reasonable security safeguards to prevent a personal data breach, and Rule 7 requires breaches to be reported to the Data Protection Board and affected people without delay, with a detailed report within 72 hours. The DPDP Rules were notified on 13 November 2025; consent manager rules apply from November 2026 and the core duties from May 2027.
None of it works without a personal data inventory. Notices, erasure requests, breach scoping and DPIAs all depend on knowing where personal data sits. Sumrite’s free PII discovery tool builds that inventory across databases, email, cloud drives and endpoints.
Definitions and the Data Protection Board of India take effect.
Registration and duties of consent managers apply.
Notice, consent, Rule 6 safeguards, Rule 7 breach reporting, retention and erasure, children’s data, rights and SDF duties.
Read the rule-by-rule DPDP Rules 2025 deadlines and safeguards checklist.
Go deeper: DPDP Act penalties · DPDP Rules 2025 timeline · PII data discovery · Consent manager vs CMP.
A simplified walk through the duties that most often involve engineering and security teams. Confirm exact obligations against the Act and the Rules.
Before processing, give a notice describing the data and purpose, and obtain consent that is free, specific, informed and unambiguous. Withdrawing consent should be as easy as giving it.
Process data only for the purpose it was collected for and erase it when it is no longer needed unless the law requires retention. This reduces both risk and breach impact.
Fiduciaries must protect personal data under their control, including data held by processors. Expect measures such as encryption, access control, monitoring, backups and regular security testing.
If a personal data breach occurs, the Data Protection Board and each affected person must be informed in the form and time set by the Rules. You need to detect and scope incidents quickly to meet that duty.
People can request access to a summary of their data, correction, erasure and grievance redress, and can nominate someone to exercise rights on their behalf. A named contact and a working grievance process are expected.
Discovery is free. Every other module builds on the inventory it creates, so you never map your data twice.
Any digital product collecting users’ personal data needs notice, consent and safeguards.
High-volume personal and financial data makes security safeguards a priority.
Sensitive categories and children’s data bring extra scrutiny.
Offering services to people in India can bring you in scope from abroad.
The work is technical. The consequences of getting India DPDP wrong show up in revenue, liability and reputation, which is why we report on it in the language of the boardroom first.
Indian consumers and enterprise buyers expect clear consent and safe handling. Weak practice costs deals.
Penalties reach ₹250 crore for failing to take reasonable security safeguards. Documented testing is useful context.
Breaches must be reported to the Data Protection Board and affected people. Tested safeguards lower that risk.
Obligations phase in over time. Starting now spreads the engineering work and avoids a rush.
Timelines are typical ranges, not promises. Yours depends on scope, team size and how much is already in place.
Run Sumrite’s free discovery tool across databases, email, cloud and endpoints to inventory every Aadhaar, PAN, mobile and bank record, and the vendors that touch it.
Replace blanket consents with purpose-specific notices and make withdrawal as easy as giving consent.
Apply encryption, masking, access control, logging and backups to the systems the inventory flagged.
Run a penetration test and fix findings, so “reasonable safeguards” has evidence behind it.
Build the 72-hour breach workflow, the rights portal and retention schedules, then rehearse them.
The Act does not prescribe a test, but the standard is “reasonable security safeguards”. When something goes wrong, being able to show that you tested, found and fixed weaknesses is the strongest answer to whether your safeguards were reasonable.
A dated penetration test report plus a retest is concrete proof that safeguards were challenged and improved.
You remain responsible for data your processors handle. Testing integrations and APIs shows where data can leak.
Finding broken access control and exposed endpoints before attackers do is the best way to avoid a reportable breach.
Penalties reflect the nature and gravity of the breach and the steps taken. Documented testing is useful context.
Consent must be specific to a purpose and easy to withdraw. A single “accept all” tick is a weak foundation.
You cannot protect, delete or report on data you cannot locate. Sumrite’s discovery tool builds the inventory for free.
Fiduciaries remain accountable for what vendors do with personal data.
Inventory, consent and security changes touch product and engineering. Starting late is how ₹250 crore exposure happens.
India DPDP is a team effort between your people, your auditor and your customers. We take the weight off all three.
From the first question about India DPDP to the final report, you deal with one accountable team and one timeline.
We have taken more than 250 clients through SOC 2 and similar audits, so we know what reviewers ask for and what they accept.
We explain what India DPDP means for your business, your roadmap and your customers before any technical work starts.
Where a third party issues the report or certificate, we route that step through local partner firms so you never have to manage a second vendor.
One accountable team takes you from scoping to retest. The people who test your systems are the people who explain the findings to your leadership.
Safeguards, consent and breach processes compared with the Act and Rules for systems holding personal data.
Expert-led testing of apps, APIs and infrastructure, including vendor integrations.
Checks that encryption, access control and logging operate as described.
Dated reports and fix records that back up your reasonable safeguards claim.
Fix guidance for engineers, then a retest confirming closure.
Personal data risk, penalty exposure and progress for leadership.
Every engagement ends with material written for two audiences: a plain-language view for executives and the board, and full technical detail for the engineers who fix things.
Where personal data is exposed and what to fix first.
Reports and retest letters that show tested and improved safeguards.
Owners and milestones aligned to the Act’s phase-in.
Each finding with an owner, severity and status.
The same Sumrite team stays with you through customer and regulatory questions.
They share ideas but differ in detail. The DPDP Act has fewer lawful grounds, a notice and consent centre, and a Data Protection Board model. Do not assume GDPR work transfers one to one.
The Schedule to the Act sets maximum penalties: up to ₹250 crore for failing to take reasonable security safeguards; up to ₹200 crore each for failing to notify the Board and affected people of a breach and for breaching the duties on children’s data; up to ₹150 crore for breaching the extra duties of a Significant Data Fiduciary; and up to ₹50 crore for breaching any other provision. The Board sets each amount based on the nature, gravity and duration of the breach.
Yes. Sumrite’s PII data discovery and inventory tool at dpdp.sumrite.com is 100% free. It runs inside your network and scans databases, email, cloud drives, file shares and endpoints for Aadhaar, PAN, passport, mobile and bank account data.
The DPDP Rules were notified on 13 November 2025. Consent manager rules apply from November 2026 and most obligations on data fiduciaries, including security safeguards and breach reporting, apply from May 2027.
Yes, when they process digital personal data outside India in connection with offering goods or services to people in India.
The Act and Rules set expectations such as encryption, access control, monitoring and backups. “Reasonable” depends on risk, so documented testing helps you justify your choices.
We run the full engagement for you and route the formal audit through our empanelled partner, so you deal with one team and get all your work done.
Browse all 23 security and compliance frameworks or see our penetration testing services.
Start with a free map of your personal data, then get a fixed-scope quote for testing and evidence.
Get the free tool → Get a Quote →