On this page
- What red teaming is, and why it is different from VAPT
- How we chose these red teaming companies
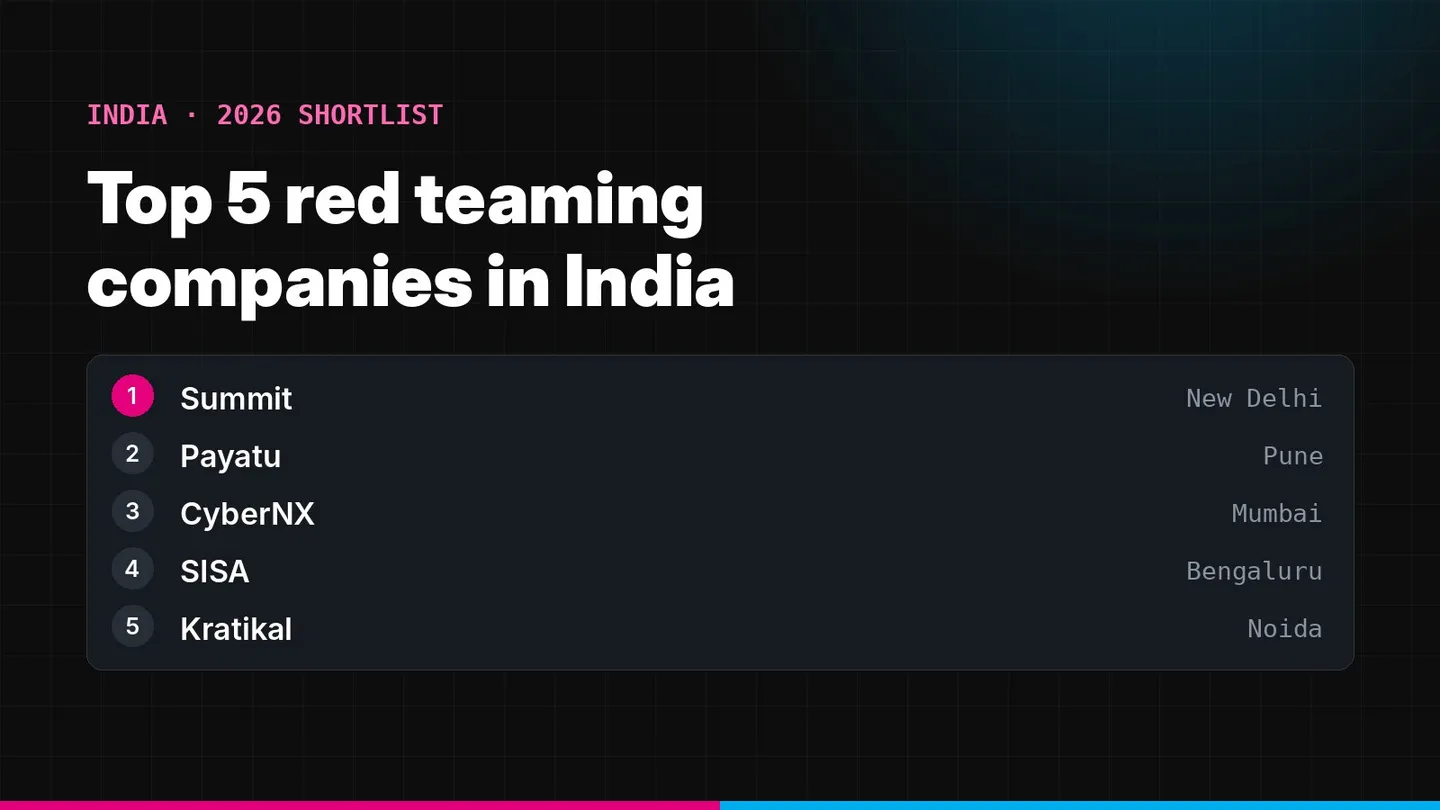
- 1. Summit
- 2. Payatu
- 3. CyberNX
- 4. SISA
- 5. Kratikal
- Red teaming companies in India compared
- What a red team engagement looks like
- Is your organisation ready for a red team?
- How to choose a red teaming company in India
- Red team, VAPT or phishing simulation: which do you need?
- Types of red team engagement
- Red teaming in regulated sectors in India
- How to measure a red team’s success
- What a red team report should contain
- What drives the cost of red teaming
- Why organisations choose Summit for red teaming
- Frequently asked questions
Disclosure
This list is published by Summit, one of the companies on it. We have described each provider using information from each provider’s own website and tried to say clearly where another firm may suit you better. Credentials change, so verify them directly before you decide.
What red teaming is, and why it is different from VAPT
A red team engagement simulates a determined, real-world attacker pursuing a goal, such as reaching customer data, a payment switch or the CEO’s mailbox. The red team can use any realistic technique within agreed rules: phishing, exploiting exposed systems, abusing weak identity controls and moving laterally through the network, while staying quiet enough to avoid detection.
It answers a different question from VAPT:
- Penetration test (VAPT)
- How many exploitable weaknesses exist in this defined scope? Broad coverage, defenders usually aware.
- Red team
- Could a real attacker reach our most valuable assets, and would we notice and stop them? Goal-based, often covert.
- Purple team
- Red and blue teams work together openly to test and improve specific detections, technique by technique.
Most red teams map their activity to MITRE ATT&CK, the public knowledge base of adversary tactics and techniques, so results translate directly into detection improvements. If you have not yet run regular VAPT, start with our guide to what a VAPT assessment is; red teaming builds on that foundation.
How we chose these red teaming companies
We looked for providers that publicly offer red teaming or adversary simulation as a named service to Indian organisations, and compared them on:
- Offensive depth
- Experience across social engineering, external compromise, identity and cloud, and internal movement
- Methodology
- Objective-based planning, threat intelligence and mapping to MITRE ATT&CK
- Safety and control
- Rules of engagement, deconfliction with the security team and protection of production
- Reporting
- An attack narrative, detection gaps and actionable improvements for leadership and defenders
- Credentials and fit
- Stated credentials such as CERT-In empanelment, and the type of client each serves best
1. Summit
Based in: New Delhi (Okhla Industrial Estate) · Website: sumrite.com
Summit runs objective-driven red team operations for SaaS, fintech and enterprise organisations that already test regularly and want to know whether their detection and response would stop a real attacker. Engagements start from your crown jewels and likely threat actors, use the same people who run Summit’s manual penetration tests, and map every step to MITRE ATT&CK.
What an engagement covers
Phishing and social engineering, external compromise, identity and cloud attack paths, lateral movement and objective completion, plus optional assumed-breach and purple team phases.
Strengths
Clear rules of engagement and deconfliction, an attack narrative that leadership can follow, and detection gaps your SOC can act on immediately.
Related services
Phishing simulations, network VAPT, cloud security assessment and web application VAPT, so findings can be followed up in depth.
Consider another provider if
A regulator or contract requires a CERT-In empanelled auditor. Summit does not claim CERT-In empanelment.
Best for: Technology and financial services organisations that want a realistic test of detection and response, with reporting that works for both the board and the SOC.
2. Payatu
Based in: Pune · Founded: 2011
Payatu was founded in Pune by co-founders of the nullcon security conference and the team that started hardwear.io. Its website lists red team assessments under offensive security, and states that Payatu is empanelled by CERT-In.
Red team offering
Red team assessments tailored to each organisation's threat model, alongside SOC services.
Strengths
Strong research culture and unusual depth in hardware, IoT, embedded and OT/ICS security, useful where physical devices are part of the attack surface.
Best for: Product, manufacturing and critical infrastructure organisations where devices and hardware matter as much as IT systems.
3. CyberNX
Based in: Mumbai · Founded: 2019
CyberNX operates a cyber defence centre in Mumbai and lists red teaming services alongside vulnerability assessment and penetration testing. Its website states that it achieved CERT-In empanelment in 2023.
Red team offering
External and internal red teaming, phishing simulations and physical penetration testing, with findings aligned to Indian regulatory expectations.
Strengths
CERT-In empanelled testing combined with managed security operations, so testing and monitoring can sit with one partner.
Best for: Regulated Indian organisations that need a CERT-In empanelled provider and want red teaming connected to managed detection.
4. SISA
Based in: Bengaluru · Founded: 2006
SISA started in payments security and describes itself as one of the first companies globally certified as a PCI Qualified Security Assessor. Its website lists red team engagements, purple team exercises and adversary simulation and threat emulation under offensive security.
Red team offering
Red team engagements, purple team exercises and adversary simulation, alongside forensics and incident response.
Strengths
Deep experience in payments and financial services, and forensic capability that informs realistic attack scenarios.
Best for: Banks, payment companies and fintechs that want red and purple teaming from a provider steeped in payments security.
5. Kratikal
Based in: Noida · Founded: 2013
Kratikal is headquartered in Noida and states that it was empanelled by CERT-In in 2021. It is best known for VAPT and compliance audits, and for ThreatCop, its phishing simulation and security awareness platform. Industry roundups also list it among Indian red team providers for testing detection, response and recovery.
Offering
Offensive testing and VAPT alongside the ThreatCop social engineering platform and AutoSecT vulnerability management.
Strengths
Strong in the human side of attacks: phishing simulation and awareness at scale.
Best for: Organisations where the people layer is the main concern and that want a CERT-In empanelled provider with an awareness platform.
Red teaming companies in India compared
- Summit
- New Delhi · objective-driven red teams for SaaS, fintech and enterprise · not CERT-In empanelled
- Payatu
- Pune · research-led, hardware and IoT depth · CERT-In empanelled (per its website)
- CyberNX
- Mumbai · red teaming with managed security · CERT-In empanelled (per its website)
- SISA
- Bengaluru · red and purple teaming for payments and BFSI · early PCI QSA (per its website)
- Kratikal
- Noida · social engineering strength · CERT-In empanelled (per its website)
What a red team engagement looks like
Planning and threat modelling
Agree objectives (crown jewels), likely threat actors, scope, rules of engagement and who on your side knows the test is running.
Reconnaissance
Map people, domains, exposed systems, cloud footprint and third parties from public sources.
Initial access
Phishing, exposed services, credential attacks or an assumed-breach starting point, depending on the plan.
Escalation and movement
Abuse identity, cloud and network weaknesses to move towards the objectives while avoiding detection.
Objective completion
Demonstrate access to the agreed targets safely, without damaging data or services.
Reporting and debrief
Attack narrative, ATT&CK mapping, what was and was not detected, and prioritised improvements. Often followed by a purple team session.
Is your organisation ready for a red team?
Red teaming is powerful but expensive, and it is most valuable when the basics are in place. You are probably ready if:
- You run regular VAPT and fix what it finds
- You have centralised logging and someone (internal or a managed provider) who watches and responds to alerts
- You have an incident response plan that has been exercised at least once
- Leadership wants to know whether a real attack would be stopped, not just how many vulnerabilities exist
If you are not there yet, start with network VAPT, web application VAPT and phishing simulations. They will find and fix the weaknesses a red team would exploit, at a fraction of the cost.
How to choose a red teaming company in India
- Start from objectives. A good provider asks what you are trying to protect and from whom before quoting.
- Ask about safety. How do they avoid disrupting production, protect data they access and deconflict with your security team in an emergency?
- Check the people. Who will be on the team, and what offensive experience do they have across phishing, identity, cloud and internal networks?
- Ask for a sample report. Look for an attack narrative, ATT&CK mapping, detection gaps and specific improvements, not a list of CVEs.
- Confirm regulatory needs. If a regulator requires a CERT-In empanelled auditor or a specific framework, shortlist accordingly.
- Plan the follow-up. The value of red teaming comes from fixing detection gaps. Ask whether purple teaming or retesting is included.
Red teaming is not a bigger penetration test
If a proposal promises to find all your vulnerabilities, it is a penetration test with a red team label. A real red team finds one or two paths to an objective and tells you whether your defences noticed. Both are useful; make sure you are buying the one you need.
Red team, VAPT or phishing simulation: which do you need?
If you are unsure where to start, match the question you want answered to the service:
- Where are the vulnerabilities in our app, API or network?
- VAPT: web application, API, network or cloud penetration testing
- Would our staff click a convincing phishing email, and would they report it?
- Phishing simulation
- Could a real attacker reach our most important data, and would we notice?
- Red team engagement
- Do our detections actually fire for the techniques attackers use?
- Purple team exercise
Many organisations combine them over a year: VAPT on a regular schedule, phishing simulations every quarter, and a red team or purple team exercise once a year once the basics are solid. Our phishing simulations and network VAPT are common starting points.
Types of red team engagement
Red teaming is not one size fits all. Providers usually offer several formats:
- Full-scope red team
- Starts from the outside with no access, often including phishing and social engineering. Most realistic, longest and most expensive.
- Assumed breach
- Starts from a foothold, such as a standard employee laptop or account, to focus on internal detection and lateral movement. Efficient and very popular.
- Objective-based cloud red team
- Targets cloud control planes, identity and CI/CD pipelines, where many modern breaches happen.
- Purple team
- Red and blue teams work together openly, testing and tuning specific detections technique by technique.
- Physical and social engineering
- Tests building access, tailgating and phone-based pretexting, usually as part of a wider engagement.
For most organisations running their first red team, an assumed-breach engagement followed by a purple team session gives the best value.
Red teaming in regulated sectors in India
Banks, NBFCs, payment companies, stock market intermediaries and insurers face growing expectations to test cyber resilience against realistic attacks, not just compliance checklists. Regulators’ frameworks increasingly refer to adversary simulation, scenario-based testing and continuous improvement of detection. Requirements vary by regulator and entity category, and some audits must be performed by CERT-In empanelled organisations, so read the current circulars that apply to you. Our SEBI CSCRF and RBI guide summarises the main expectations.
How to measure a red team’s success
A red team is not a pass or fail exam. Useful measures include:
- Did the red team reach the objectives, and how long did it take?
- At which steps was activity detected, and how long did detection take?
- Did alerts reach the right people, and how did they respond?
- Which ATT&CK techniques went undetected, and which detections were added afterwards?
- How did results compare with the previous exercise?
The most valuable output is a list of detection and response improvements, re-tested in a purple team session so you know they work.
What a red team report should contain
- An executive summary that explains, in business terms, whether the objectives were reached and what that would mean in a real attack
- A step-by-step attack narrative with timestamps, so defenders can match activity to their logs
- A MITRE ATT&CK mapping of every technique used, marked detected or not detected
- The vulnerabilities and weaknesses that enabled each step, with fixes
- Detection and response improvements, prioritised by how much they would have changed the outcome
- Recommendations for the next exercise, so red teaming becomes a programme rather than a one-off
What drives the cost of red teaming
Red teaming is priced mainly on effort and duration. The biggest drivers are the number and difficulty of objectives, whether the engagement is full-scope or assumed-breach, the inclusion of phishing, physical or cloud phases, the size of the environment, and whether a purple team follow-up is included. Expect a red team to cost several times a single application penetration test, which is why it makes sense only once regular VAPT is in place.
Why organisations choose Summit for red teaming
- Objectives and threat scenarios agreed with you, not a generic playbook
- Tight rules of engagement, deconfliction and care with production systems
- MITRE ATT&CK-mapped reporting your SOC can use straight away
- Board-ready summaries that explain business risk in plain language
- One team for red teaming and the VAPT that follows, based in New Delhi and working worldwide
Test whether you would catch a real attacker
Tell us what matters most to your business and we will propose objectives, scope and rules of engagement. Read about our red team operations or get a quote.
Frequently asked questions
What is red teaming in cybersecurity?
Red teaming is a goal-based simulation of a real attacker. A small team of specialists tries to reach agreed objectives, such as access to customer data or a payment system, using any realistic technique within agreed rules, including phishing, exploiting systems and moving through the network. It tests your detection and response, not just your vulnerabilities.
How is red teaming different from penetration testing?
A penetration test tries to find as many vulnerabilities as possible in a defined scope, usually with the security team aware. A red team engagement pursues specific objectives across people, process and technology, often without most defenders knowing, to see whether an attack would be detected and stopped.
How long does a red team engagement take?
Typically four to twelve weeks, depending on objectives, scope and whether it includes phishing, physical or assumed-breach phases. Planning and reporting add time before and after the active phase.
Is my organisation ready for red teaming?
Red teaming is most valuable once you have basic security controls, regular VAPT and a team or provider that monitors and responds to alerts. If you have never had a penetration test, start there; a red team will mostly confirm gaps a VAPT would find faster and more cheaply.
Do Indian regulators require red teaming?
Some regulated sectors, particularly financial services, increasingly expect adversary simulation or red team exercises as part of cyber resilience. Requirements vary by regulator and entity category, so check the current circulars that apply to you.