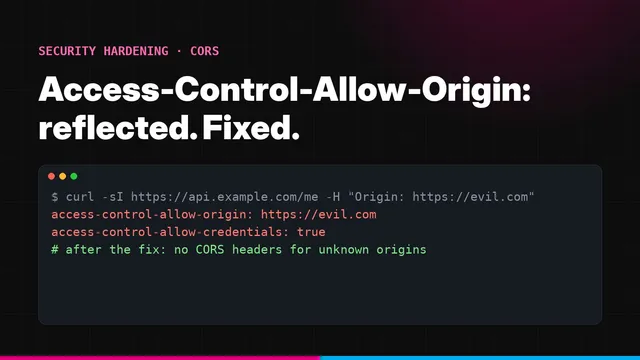
Your API reflects any Origin in Access-Control-Allow-Origin. Here is how to fix it.
We sent Origin: evil.com and the API echoed it back with credentials allowed. Why that matters and how to fix it in every common stack.
10 min read
Category
Step-by-step fixes for findings that appear in almost every VAPT report, from information-disclosure headers to cloud misconfigurations.
We sent Origin: evil.com and the API echoed it back with credentials allowed. Why that matters and how to fix it in every common stack.
10 min read
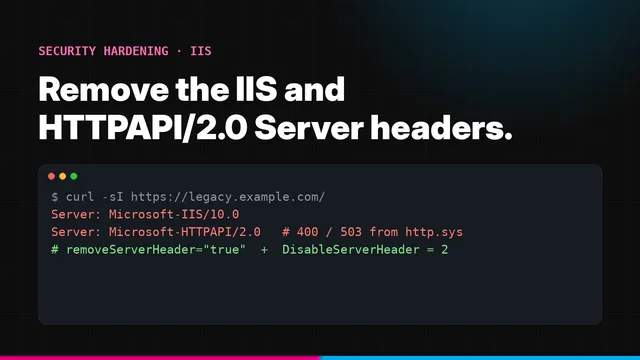
Microsoft-IIS/10.0 and Microsoft-HTTPAPI/2.0 both reveal your stack. They come from different layers and need different fixes. Here are both.
10 min read
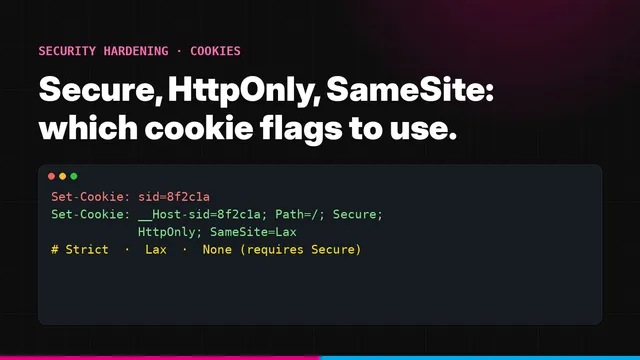
Secure, HttpOnly, SameSite Strict, Lax or None: what each flag does, which one each cookie should use, and how to set them in your stack.
8 min read
The server: awselb/2.0 header tells attackers what you run. One listener attribute removes it. Console, CLI and Terraform steps.
3 min read
Talk to a tester
Scoped quote within a day. Manual testing, verified findings, a fix-and-retest cycle and a report your auditors accept.