On this page
Need a CERT-In empanelled VAPT report? We run the full engagement for you and route the formal attestation through our CERT-In empanelled partner, so you deal with one team from scoping to report.
“Is your firm CERT-In empanelled?” is one of the first questions Indian buyers ask a VAPT provider. It is often the wrong first question. Some organisations genuinely need an empanelled auditor’s report; many others are paying for a label nobody asked them for. This guide separates the two.
What CERT-In empanelment means
CERT-In (the Indian Computer Emergency Response Team) is the national agency for cyber security incidents under the Ministry of Electronics and Information Technology. Among its functions, it maintains a panel of information security auditing organisations.
To get on the panel, a firm is evaluated on its audit track record, its methodology, the size and qualifications of its in-house technical team, and practical vulnerability assessment and penetration testing skill tests. Empanelled firms are expected to follow CERT-In’s audit guidelines and code of conduct, and can be suspended or removed for poor performance.
- Maintained by
- CERT-In, Ministry of Electronics and Information Technology
- What is empanelled
- The auditing organisation, not your company or your system
- Who issues your report
- The empanelled auditor, on its own letterhead
- How to verify
- The current list of empanelled organisations on the CERT-In website
- Typical frequency
- At least annually and after major changes, unless your regulator says otherwise
Two points cause most of the confusion:
- CERT-In does not certify your company. There is no “CERT-In certified” status for an application or an organisation. What you receive is an audit report, and where needed an audit certificate or compliance letter, issued by the empanelled firm.
- Empanelment is about the auditor, not the depth of the test. Two empanelled firms can deliver very different work. Empanelment tells you the firm passed CERT-In’s evaluation; the statement of work and the report tell you what was actually tested.
Who actually requires a CERT-In empanelled auditor
Government and public sector
Ministries, departments, PSUs and public bodies commonly require security audits of their applications and websites by CERT-In empanelled auditors before go-live and periodically after.
Government-hosted websites
Sites hosted on government infrastructure typically need a security audit clearance from an empanelled auditor before they can be put into production.
Regulated financial entities
Where a regulator names CERT-In empanelled auditors, as SEBI does for the cyber audit of regulated entities under its CSCRF, the audit must be done by a firm on the panel.
Tenders and contracts
Government and enterprise tenders often make a CERT-In empanelled audit report a pre-qualification or go-live condition for vendors.
If you are a private SaaS company selling to other private companies, you usually need a good independent VAPT report for SOC 2, ISO 27001 or a customer questionnaire, not an empanelled one. Read the actual requirement before you narrow your vendor list: the wording in a circular, tender or contract decides it, not the general reputation of empanelment. Our guide to which compliance frameworks require penetration testing covers the non-government cases.
Check the exact wording
Requirements are usually phrased as “audit by a CERT-In empanelled auditor”, “security audit clearance certificate” or “audit as per CERT-In guidelines”. These are not the same thing. The last one may be met by following CERT-In’s guidelines without an empanelled firm. Ask the requesting party which document they need before you scope the work.
What a CERT-In audit covers
CERT-In’s audit guidelines push away from scanner-only work. Audits are expected to look for all known vulnerability classes rather than a top-10 list, include manual testing, and have the testers’ work reviewed by a separate person before the report is issued. In practice, a CERT-In style VAPT of a web application or API covers:
- Authentication, session management and access control, including tests for one user reaching another user’s data
- Input handling: injection, cross-site scripting, file upload and deserialisation issues
- Business logic, such as skipping payment or approval steps
- Server and platform configuration: TLS, headers, exposed services and default credentials
- Sensitive data exposure in responses, logs and client-side code
- A retest after fixes, with the closure status of each finding recorded
For infrastructure the same principle applies: external and internal network testing, configuration review and verification of fixes. Our web application VAPT guide explains the testing in more depth.
What the report and certificate must show
When a third party asks for your CERT-In audit, they will look for:
- The auditor’s identity. The empanelled organisation’s name, matching the CERT-In list, on the report and certificate.
- Scope. The exact URLs, IP addresses, application versions or builds tested, and the dates.
- Methodology. The standards followed and whether testing was manual, automated or both.
- Findings. Each issue with severity, evidence, impact and a specific fix.
- Retest status. Which findings were closed and verified. Many clearance certificates are issued only once high and critical issues are fixed.
- Sign-off. Signatures from the audit team and the reviewer.
A certificate that names a different domain, an older version of your app or a firm not on the list will usually be rejected. Plan the audit against the system that will actually go live.
How to choose a provider for CERT-In empanelled VAPT
- Confirm you need empanelment. Get the requirement in writing from the regulator, department or customer.
- Verify the issuing organisation. Check the current CERT-In list and confirm whose name will be on the report.
- Ask how much is manual. Ask for a sample report with redacted findings and look for evidence of hands-on testing.
- Agree on the retest. Confirm that a retest and an updated report or certificate are included, and how long you have to fix issues.
- Lock the scope. List every URL, API and environment, and test the version that will go to production.
- Plan for timelines. Build in time for fixes before the certificate is issued, especially for go-live deadlines.
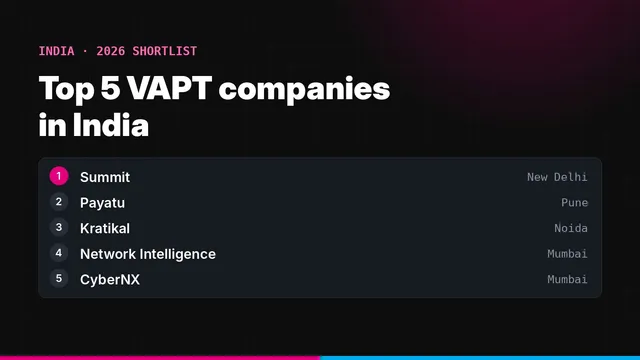
Price is driven by scope, not by empanelment alone. See our VAPT cost guide and our comparison of VAPT companies in India.
How Summit delivers CERT-In empanelled VAPT
Summit is based in New Delhi and runs manual, expert-led VAPT for Indian and international companies. When you need a CERT-In empanelled audit, we run the whole engagement: scoping, testing of your web applications, APIs, mobile apps and networks, remediation support and the retest. The formal attestation is routed through our CERT-In empanelled partner, so you get the empanelled report your regulator or customer needs without managing a second vendor.
Need a CERT-In empanelled report on a deadline?
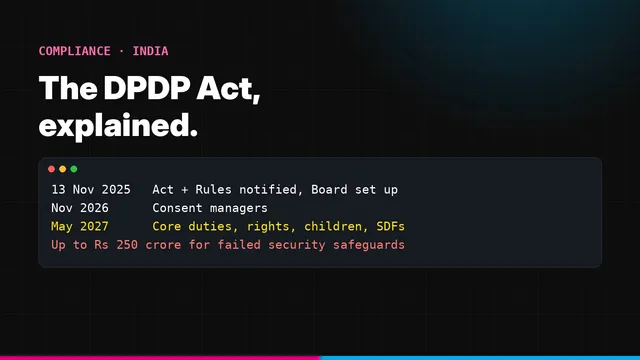
Tell us what you need to submit and by when. We will scope the audit, test, help you fix and deliver the report. Get a quote or read our India DPDP guide.
Related reading: DPDP Rules 2025 deadlines and safeguards · What is a VAPT assessment? · What makes a VAPT report worth paying for
Frequently asked questions
What is a CERT-In empanelled auditor?
An information security auditing organisation that CERT-In, India's national Computer Emergency Response Team under MeitY, has evaluated and placed on its published panel. Empanelment covers the organisation's audit experience, methodology, team and practical testing skills. CERT-In maintains the list but does not assign auditors; you choose a firm from it.
Is CERT-In empanelled VAPT mandatory?
Only where a regulator, government body or contract asks for it. Common cases are government and public sector systems, websites hosted with government infrastructure, regulated financial entities whose regulator names CERT-In empanelled auditors, and tenders that specify it. For SOC 2, ISO 27001 or customer due diligence, empanelment is not required.
Does CERT-In issue a certificate to my company?
No. CERT-In does not audit or certify individual organisations through empanelment. The empanelled auditor performs the audit and issues the report and, where requested, an audit certificate or compliance letter on its own letterhead.
How do I check that a provider is CERT-In empanelled?
Look the organisation up on the current list of empanelled information security auditing organisations published on CERT-In's website, and confirm that the report and certificate you will receive are issued in that organisation's name.
How often does a CERT-In audit need to be done?
CERT-In's audit guidelines call for audits at least once a year and after major changes to critical infrastructure or applications. Your regulator, sector rules or contract may set a different frequency, so follow whichever is stricter.
Can Summit deliver a CERT-In empanelled VAPT report?
Yes. Summit runs the full engagement, from scoping and manual testing to the retest, and routes the formal attestation through our CERT-In empanelled partner, so you deal with one team from scoping to report.
Faisal Khan is a Director at Summit, where he oversees penetration testing, risk assessment and compliance engagements for SaaS and enterprise clients. Case studies are anonymised and published with client permission.