On this page
Need a CERT-In empanelled audit? Sumrite runs the full engagement and delivers the empanelled report through our CERT-In empanelled partner. Talk to our team or read our guide to CERT-In empanelled VAPT.
AMBAK has drawn a lot of attention since its launch, and a lot of misreporting. Since April, articles have described a blockchain verification portal, QR-coded certificates and a fixed go-live date, none of which we could trace to CERT-In or the Ministry. This guide separates the two, and sets out what auditees and empanelled auditors should do while CERT-In publishes the detail.
What AMBAK is
AMBAK stands for Audit Monitoring, Benchmarking, Analysis and Kinetic Interventions. It is a CERT-In platform for oversight of cyber security audits in India. The four parts of the name describe its stated purpose:
- Audit Monitoring
- Tracking the security audits that CERT-In empanelled auditing organisations perform.
- Benchmarking
- Comparing audits and audit practice against a common standard, across auditors and sectors.
- Analysis
- Using audit data to identify patterns, recurring weaknesses and risk trends.
- Kinetic Interventions
- Acting on what the analysis shows, through targeted interventions.
CERT-In (the Indian Computer Emergency Response Team) is India’s national nodal agency for cyber security incidents, part of the Ministry of Electronics and Information Technology (MeitY). It also runs the empanelment of information security auditing organisations, the panel of firms allowed to describe themselves as CERT-In empanelled auditors. AMBAK sits on top of that system: it is about how CERT-In oversees the audits those firms produce.
Where and when it was launched
AMBAK was launched at CERT-In SAMVAAD 2026, CERT-In’s three-day national annual conference, held from 27 to 29 April 2026 at the BITS Pilani K. K. Birla Goa Campus and organised with BITS Pilani, Goa. More than 500 delegates attended, including representatives of CERT-In empanelled auditing organisations.
The Government of India’s PIB press release on the conference lists the launch of AMBAK among the event’s landmark developments, alongside progress reports from CERT-In’s working groups on emerging domains and a cyber security certification course for rural financial institutions with BIRD and NABARD. Coverage of the conference records CERT-In Senior Director S. S. Sarma describing SAMVAAD as a platform for auditing organisations to upgrade their practices.
What is confirmed and what is not
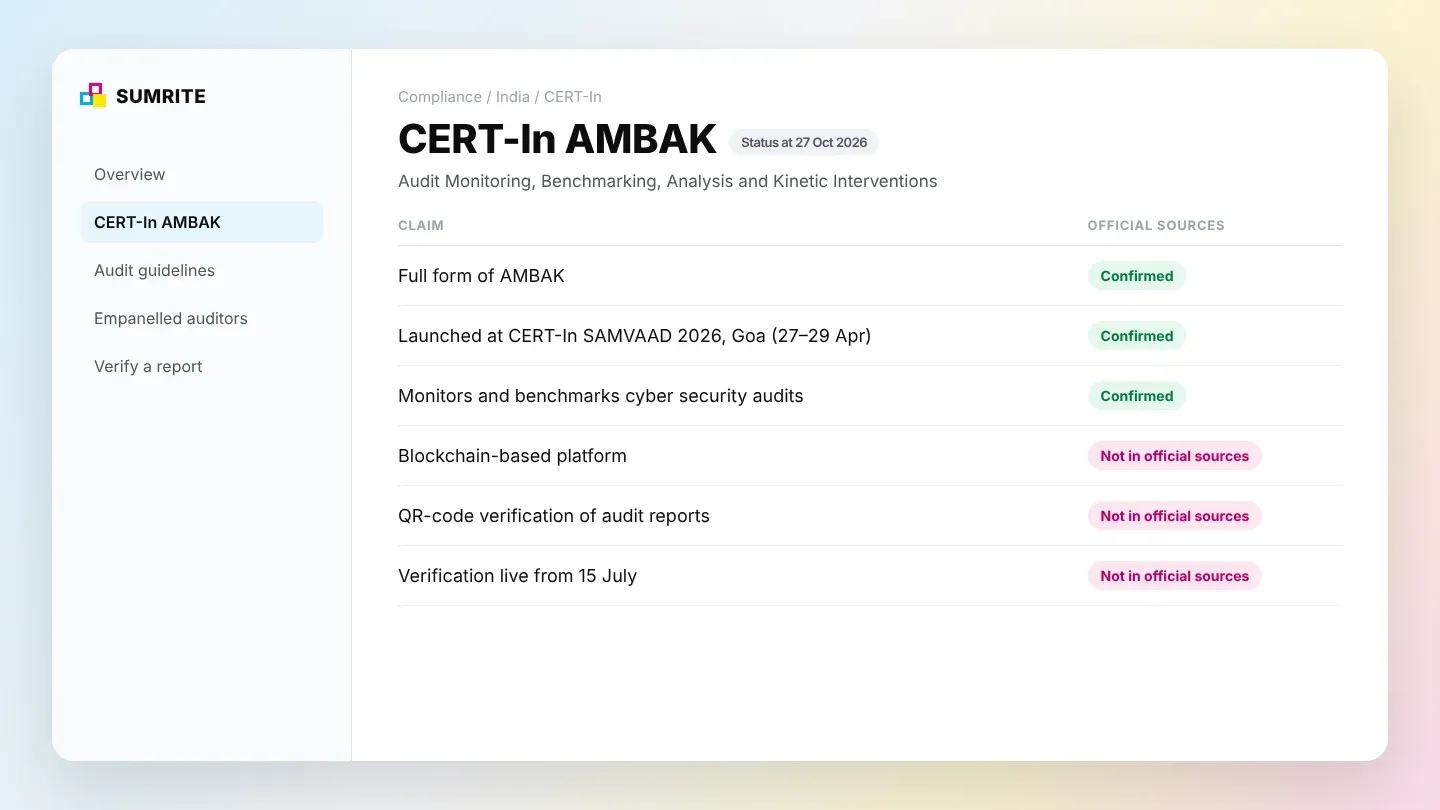
As of 27 October 2026, this is how the main claims about AMBAK stand against official sources: the PIB release and CERT-In’s own empanelment page.
| Claim | Status | Source |
|---|---|---|
| AMBAK stands for Audit Monitoring, Benchmarking, Analysis and Kinetic Interventions | Confirmed | PIB release |
| Launched at CERT-In SAMVAAD 2026, Goa, 27 to 29 April 2026 | Confirmed | PIB release |
| It concerns the monitoring and benchmarking of cyber security audits | Confirmed by the name and launch context | PIB release, conference coverage |
| AMBAK is a blockchain-enabled platform | Not in official sources | Vendor articles only |
| Audit reports and certificates carry QR codes verifiable through AMBAK | Not in official sources | Vendor articles only |
| Report verification through AMBAK began on 15 July | Not in official sources | Vendor articles only |
| Auditees must register on AMBAK | Not announced | No published requirement |
| A public AMBAK portal URL | Not published on CERT-In’s empanelment page | Checked 27 October 2026 |
Be careful with AMBAK links and 'AMBAK-verified' badges
CERT-In has not published an AMBAK verification mark, criteria or portal address on its empanelment page. Treat any link, badge or “AMBAK-verified” claim sent by a vendor as unverified until you can match it to cert-in.org.in. If you need a firm answer, write to CERT-In’s empanelment team through the contact details on its website.
None of this means the unconfirmed features will not arrive. Central verification of audit reports would fit AMBAK’s purpose and would solve a real problem: forged and over-scoped audit certificates. But compliance commitments, procurement clauses and board reporting should rest on what CERT-In has published, not on what a vendor expects.
Why CERT-In wants audit monitoring
AMBAK follows a run of changes that raised the bar for CERT-In audits:
- CERT-In Directions, 28 April 2022. Six-hour incident reporting, log retention and related duties. Audits are expected to check compliance with them.
- Comprehensive Cyber Security Audit Policy Guidelines, 25 July 2025. According to AZB & Partners’ analysis, the guidelines require audits at least annually, findings mapped to CWE and CVE and rated with CVSS supplemented by EPSS, a final report only after vulnerabilities are closed and a follow-up audit is done, audit data kept on systems in India, auditor fees that do not depend on the outcome, and audit metadata and reports shared with CERT-In within five days of completion.
- A new empanelment round. CERT-In accepted new applications for empanelment from 1 July to 30 September 2026, according to its empanelment page.
The five-day reporting rule is the important link. Once every empanelled auditor sends audit metadata to CERT-In, CERT-In holds a national dataset of audits. AMBAK is the platform to monitor that data, benchmark auditors against each other and intervene where audits fall short. In practice, that means weak, rushed or rubber-stamp audits become easier to spot.
What AMBAK means for organisations being audited
For now, nothing in your obligations has changed. CERT-In has not announced any new requirement for auditees under AMBAK. What has changed is the direction of travel: the quality of the audit you buy is more likely to be checked.
- Keep running audits on the cycle your regulator and the July 2025 guidelines require: at least annually, and before major changes go live
- Choose an auditor on audit quality and evidence, not on the lowest price for a certificate
- Expect your audit metadata to reach CERT-In within five days of the audit closing
- Make sure the final report covers production, or clearly states that only staging was tested
- Fix critical and high findings and complete the follow-up audit before you rely on the report
- Do not sign contracts or answer tenders that depend on AMBAK features CERT-In has not published
What it means for empanelled auditors
Benchmarking cuts both ways. Auditors with thorough methodology, complete evidence and real retests have nothing to fear from it. Auditors that sell certificates without testing, or reuse findings across clients, are exactly what audit monitoring is designed to catch. CERT-In’s July 2025 audit guidelines already provide for watch-listing, suspension and debarment of auditors that do not comply.
If you buy audits, this is a reason to check how your auditor works, not only whether it is on the list.
How to verify a CERT-In audit report today
Until CERT-In publishes a verification service, verify a report the way you would have before AMBAK:
- Check the list. Confirm the issuing organisation appears on CERT-In’s current list of empanelled information security auditing organisations, published from the empanelment page, and that it was empanelled on the audit dates.
- Match the legal entity. The report must be issued in the empanelled organisation’s own legal name, not a reseller’s or partner’s.
- Check the scope. Application, environment, versions or hash values and the test window should match the system you rely on.
- Check the content. Findings mapped to CWE and CVE, CVSS and EPSS ratings, closure status and a follow-up audit, as the July 2025 guidelines require.
- Confirm with the auditor. Ask the issuing firm to confirm the report reference, using contact details you found yourself, not ones printed on the document.
- Watch for red flags. Wording such as “CERT-In certified”, a CERT-In logo or a “certificate” with no full report behind it.
Our guide to CERT-In empanelled VAPT covers who needs an empanelled audit and what the report must show, and what makes a VAPT report worth paying for covers report quality more broadly.
How Sumrite helps
Sumrite is a New Delhi cybersecurity company, founded in 2007, that runs manual, expert-led security testing of web applications, APIs, mobile apps and networks. When you need a CERT-In empanelled audit, we run the whole engagement, from scoping and testing to remediation support and the follow-up audit, and deliver the empanelled report through our CERT-In empanelled partner. Every report is built to the July 2025 guidelines: CWE and CVE mapping, CVSS and EPSS ratings, evidence for each finding and a retest, the kind of audit that benchmarking is meant to reward.
We will update this page as CERT-In publishes more about AMBAK.
Get an audit that stands up to scrutiny
Tell us what you need to submit and to whom. We will scope the audit, test, help you fix and deliver the CERT-In empanelled report. Get a quote or run the free scan first.
Related reading: CERT-In empanelled VAPT · How often should you run a penetration test? · SEBI CSCRF VAPT requirements · RBI VAPT requirements
Frequently asked questions
What is CERT-In AMBAK?
AMBAK stands for Audit Monitoring, Benchmarking, Analysis and Kinetic Interventions. It is a platform CERT-In, India's national cyber security agency under the Ministry of Electronics and IT, launched at the CERT-In SAMVAAD 2026 conference in Goa (27 to 29 April 2026) to support the monitoring, benchmarking and analysis of cyber security audits carried out by CERT-In empanelled auditors.
What is the full form of AMBAK?
Audit Monitoring, Benchmarking, Analysis and Kinetic Interventions.
When and where was AMBAK launched?
At CERT-In SAMVAAD 2026, CERT-In's national annual conference for security auditing organisations, held from 27 to 29 April 2026 at the BITS Pilani K. K. Birla Goa Campus. The Government of India's PIB release on the conference lists the AMBAK launch among its key outcomes.
Is AMBAK blockchain-based, and can I verify audit reports by QR code?
Not according to any official source we could find. Some vendor articles describe AMBAK as a blockchain platform with QR-code verification of audit reports from 15 July. As of 27 October 2026, neither the PIB release nor CERT-In's empanelment page mentions blockchain, QR codes or a verification start date, so treat those claims as unconfirmed.
Do companies being audited need to register on AMBAK?
CERT-In has not published any registration, onboarding or compliance requirement for auditees under AMBAK. Your obligations still come from CERT-In's Comprehensive Cyber Security Audit Policy Guidelines of July 2025, the CERT-In Directions of April 2022 and your sector regulator.
How do I verify a CERT-In audit report today?
Check that the issuing organisation appears on CERT-In's current list of empanelled information security auditing organisations, that the report is issued in that organisation's legal name, that its scope, environment, versions and test dates match the system you rely on, and confirm the report reference directly with the auditor using contact details you found yourself.
Does AMBAK change how often we need a CERT-In audit?
No change has been announced. CERT-In's July 2025 audit guidelines call for a cyber security audit at least once a year, and before major changes go live, with sector regulators able to require more.
Faisal Khan is a Director at Sumrite, where he oversees penetration testing, risk assessment and compliance engagements for SaaS and enterprise clients. Case studies are anonymised and published with client permission.