On this page
Who is asking
- DIFC
- Data protection law for firms established in the centre. See [DIFC and ADGM](/compliance/difc-adgm/).
- ADGM
- Data Protection Regulations 2021 for firms in the Abu Dhabi Global Market.
- CBUAE
- Information-security expectations for regulated financial institutions.
- UAE PDPL
- Federal personal data law. See [UAE PDPL](/compliance/uae-pdpl/).
- Enterprise buyers
- Vendor questionnaires that ask for a recent third-party test.
What the report should contain
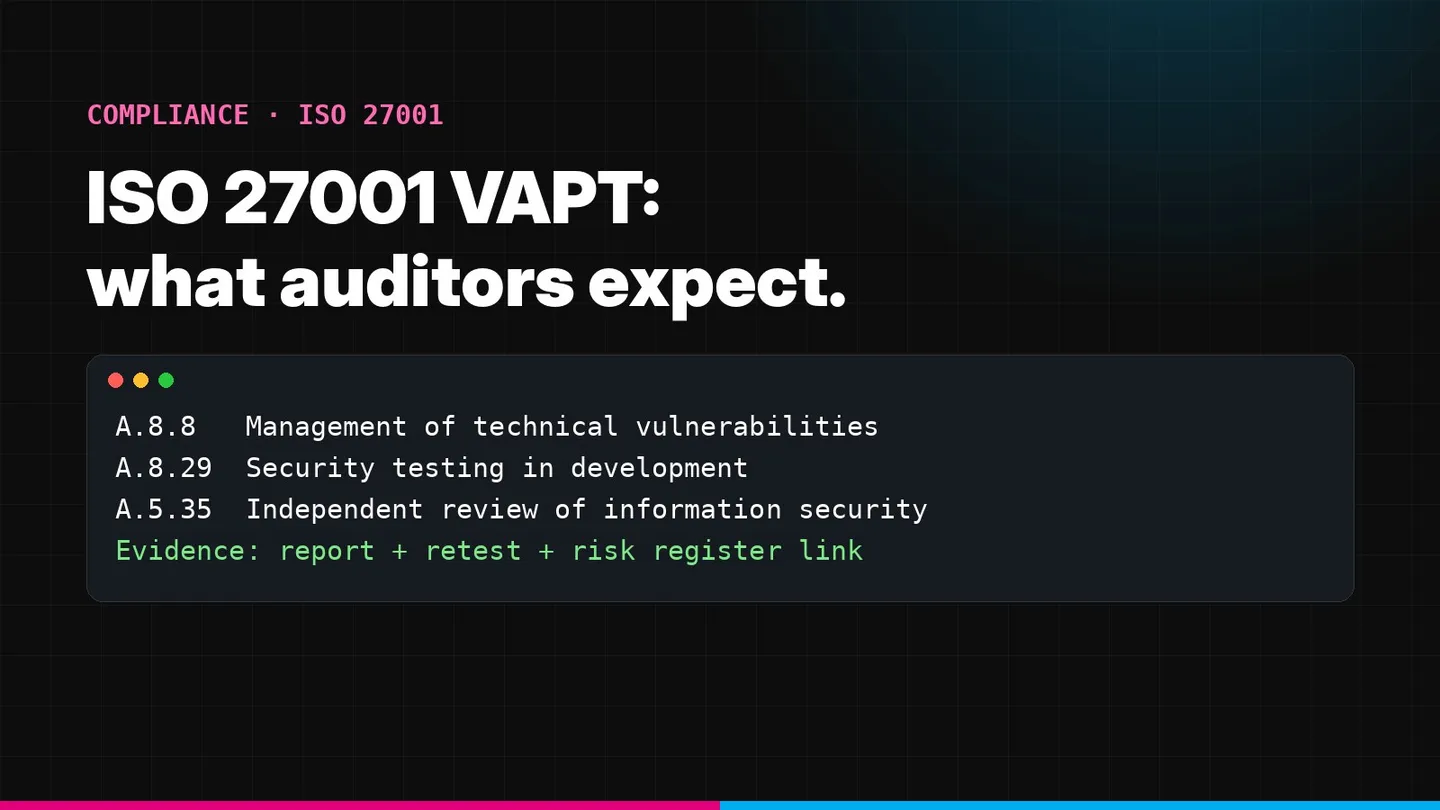
- Scope listing the tested assets and environments
- Methodology and testing dates
- Each finding verified, with severity, evidence and reproduction steps
- Remediation advice specific to your stack
- A retest section showing closed findings
- Findings that expose personal data flagged for privacy owners
A scanner export will not answer these; see what makes a VAPT report worth paying for.
Scoping tips for UAE teams
- Identify which regime covers your entity: DIFC, ADGM or federal.
- List customers and regulators who will read the report.
- Scope web, API, mobile and cloud assets that handle personal or financial data.
- Agree the retest date before you start.
See the UAE regional page and the framework overview.
Send us the UAE questionnaire
We will scope the test that produces the evidence. Request a quote.
Frequently asked questions
Do DIFC and ADGM follow the federal UAE PDPL?
Generally no. DIFC and ADGM have their own data protection regimes. Check which regime covers your entity and activity before choosing how to map the report.
What do UAE reviewers expect from a VAPT report?
Named assets, methodology, verified findings with severity, evidence, remediation and a retest, written so a procurement or regulatory reviewer can map them to their controls.
How fast can a VAPT report be delivered for a UAE company?
A scoped web application or API assessment is delivered in 48 hours, including the report. Broader cloud, network or mobile scopes take longer.
Does Summit serve Dubai and Abu Dhabi companies?
Yes. Summit delivers VAPT reports for UAE teams, mapped to DIFC, ADGM, CBUAE and UAE PDPL expectations, with an NDA before any technical discussion.
Faisal Khan is a Director at Summit, where he oversees penetration testing, risk assessment and compliance engagements for SaaS and enterprise clients. Case studies are anonymised and published with client permission.