On this page
The environment
The firm runs a typical modern office network: a next-generation firewall as the central gateway, a primary and secondary Active Directory, file and remote-desktop servers on a virtualisation host, and separate segments for staff desktops, Wi-Fi, CCTV cameras and biometric door controllers. The test was a grey-box internal assessment with an administrative Windows account, following NIST SP 800-115, combining scanning with manual confirmation of every issue.
What was done well
Segmentation was real, not just on a diagram. User, wireless and IoT devices sat in their own zones behind the firewall, which limits how far any single compromise can spread. That is the hardest part to get right, and it was right.
What we found
Factory passwords on network switches and a printer
Several network switches accepted their manufacturer’s default username and password on the web management interface, and so did the office printer. Default credentials are published online, so anyone on the network could log in.
Admin access to a switch means changing VLANs, mirroring traffic or disabling protections, which is exactly the segmentation the firm had worked to build. Admin access to a printer exposes scanned documents and address books.
Fix: unique, strong credentials on every device, management interfaces reachable only from an admin network, and a device inventory that checks for defaults whenever new hardware arrives.
An unpatched Windows service: QueueJumper
One host ran Microsoft Message Queuing without the patch for CVE-2023-21554 (QueueJumper). The flaw lets an attacker who can reach the service run code on the server without logging in.
Fix: apply the Windows update, and disable Message Queuing wherever no application needs it.
SMB signing not required
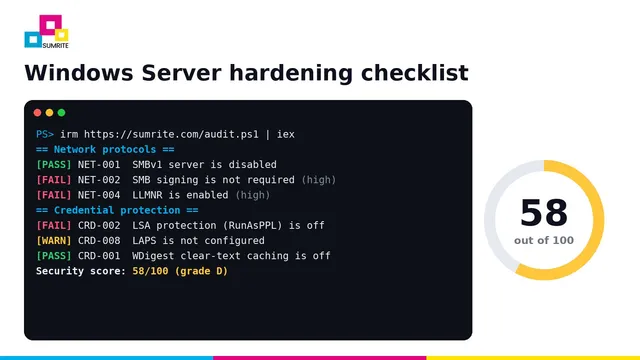
File-sharing traffic did not require signing. On a network where an attacker can capture authentication, unsigned SMB lets them relay credentials to other servers.
Fix: require SMB signing on all servers and workstations through Group Policy.
Weak TLS ciphers (SWEET32)
A service still offered 64-bit block ciphers such as 3DES, which are vulnerable to the SWEET32 attack on long-lived connections.
Fix: remove 3DES and other legacy ciphers and allow only modern TLS configurations.
Why these four matter together
None of these issues required an exotic exploit. A default password on a switch undoes segmentation; an unpatched service gives a server; unsigned SMB spreads credentials. This is how attackers move through networks that look strong on paper.
Checklist for any office network
- No device keeps its factory password, including switches, printers, cameras and door controllers
- Management interfaces reachable only from an admin segment
- Monthly Windows patching, with unused services disabled
- SMB signing required everywhere
- Legacy TLS ciphers removed
- Segmentation verified by testing, not just by design
Sumrite runs network penetration testing and red team operations for businesses in Saudi Arabia, the UAE and worldwide. Read this case study in Arabic.
Frequently asked questions
Why are default passwords on switches and printers so dangerous?
Network switches control VLANs and routing, so an attacker with admin access can move between segments, sniff traffic or switch off protections. Printers often store scanned documents and address books. Factory passwords are public, so anyone on the network can log in.
What is QueueJumper (CVE-2023-21554)?
A remote code execution flaw in Microsoft Message Queuing. An attacker who can reach the service can run code on the server without logging in. Microsoft patched it in 2023; the fix is to patch or disable the service where it is not needed.
What does 'SMB signing not required' mean?
Without required signing, SMB traffic between machines can be intercepted and relayed. Attackers use this to reuse captured credentials against other servers. Requiring signing on all hosts closes the relay path.
Does good network segmentation make a penetration test unnecessary?
No. Segmentation limits how far an attacker can move, but it does not stop one weak device inside a segment from becoming the foothold. Testing finds those weak points.