On this page
Why enterprise deals ask for a pentest
A large customer is trusting you with their data. Their security team cannot inspect your code, so they ask for independent evidence: a recent penetration test report, a summary of findings and proof that issues were fixed. If you cannot provide it, the deal waits in procurement.
What to test, in order
- The web application, with real roles. Test as an admin, a standard user and a read-only user. Most serious SaaS flaws are authorisation flaws between roles.
- Tenant isolation. Use two tenant accounts and try to read, change or delete the other one’s data. This is the failure enterprise buyers fear most.
- The API. The API is usually the real product. Test object-level and function-level authorisation. See API security testing.
- Cloud configuration. Storage, IAM, network exposure and secrets. See cloud security assessment.
- Mobile apps and integrations, if you ship them.
What the report must show
Reviewers read for scope, method, verified findings with evidence, remediation and retest status. They notice when a report is a scanner export; see what makes a VAPT report worth paying for. Run our free scan at scan.sumrite.com first so the scanner-level items are already closed before expert testing starts.
Timing
- Test before the first enterprise deal, with enough time to fix and retest
- Re-test after major releases, new payment flows or architecture changes
- Align the test with your SOC 2 or ISO 27001 window so one report serves several purposes
- Keep every report and retest letter as audit evidence
See also SOC 2 and the VAPT report and which frameworks require penetration testing.
Need the SOC 2 report itself? We run the full engagement for you and route the formal attestation through our network of licensed CPA partner firms, so you deal with one team from readiness to report.
Need a report for a deal?
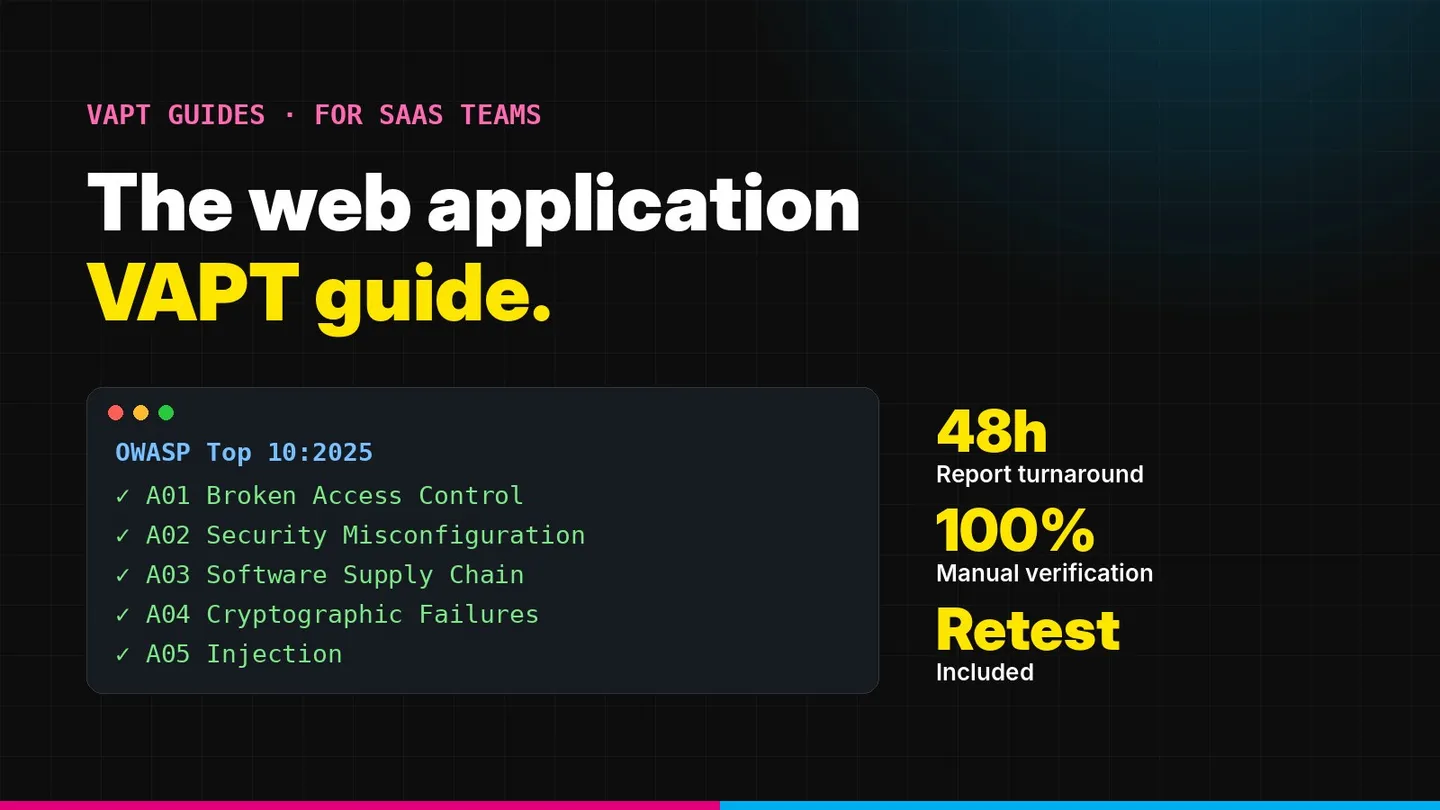
Send us your scope and the buyer’s questionnaire. We will quote in about 15 minutes and deliver an expert-verified report in 48 hours for a scoped web or API test. Get a quote.
Frequently asked questions
When should a SaaS startup get its first VAPT?
Before the first enterprise deal, not during it. Procurement reviews move much faster when you can attach a recent penetration test report and a retest, rather than promising one after signature.
What should a startup test first?
The customer-facing web application and its API, tested with real roles and at least two tenants. Add a cloud configuration review once you run production on AWS, Azure or GCP.
Does a startup need SOC 2 to sell to enterprises?
Not always, but many enterprise buyers ask for SOC 2 or an equivalent. A recent third-party penetration test is often the minimum evidence they accept while SOC 2 is in progress.
How often should a SaaS company repeat VAPT?
At least annually, and after major releases, new payment flows or cloud migrations. Keep each report and retest for your audit evidence.
Faisal Khan is a Director at Summit, where he oversees penetration testing, risk assessment and compliance engagements for SaaS and enterprise clients. Case studies are anonymised and published with client permission.